
Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?
An engineer is implementing NTP authentication within their network and has configured both the client and server devices with the command ntp authentication-key 1 md5 Cisc392368270. The server at 1.1.1.1 is attempting to authenticate to the client at 1.1.1.2, however it is unable to do so. Which command is required to enable the client to accept the server’s authentication key?
A Cisco FTD engineer is creating a new IKEv2 policy called s2s00123456789 for their organization to allow for additional protocols to terminate network devices with. They currently only have one policy established and need the new policy to be a backup in case some devices cannot support the stronger algorithms listed in the primary policy. What should be done in order to support this?
What is a commonality between DMVPN and FlexVPN technologies?
An MDM provides which two advantages to an organization with regards to device management? (Choose two)
A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
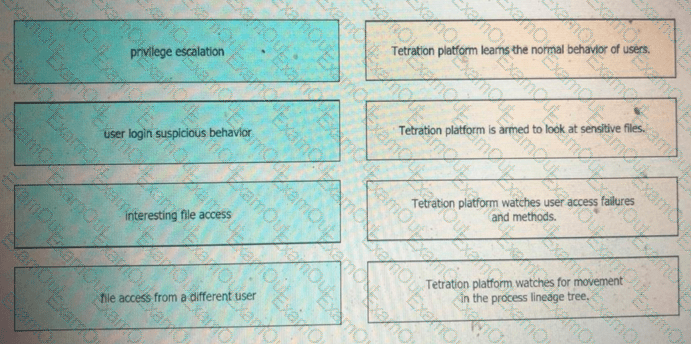
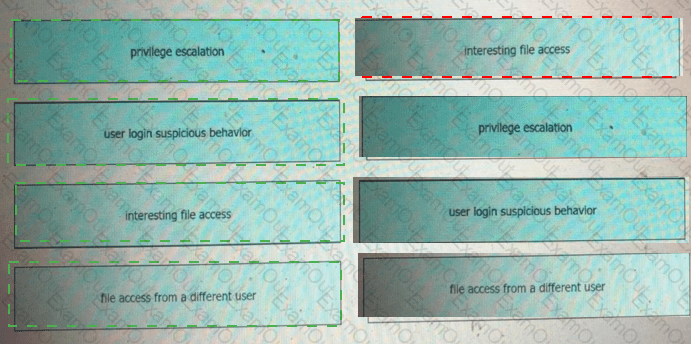
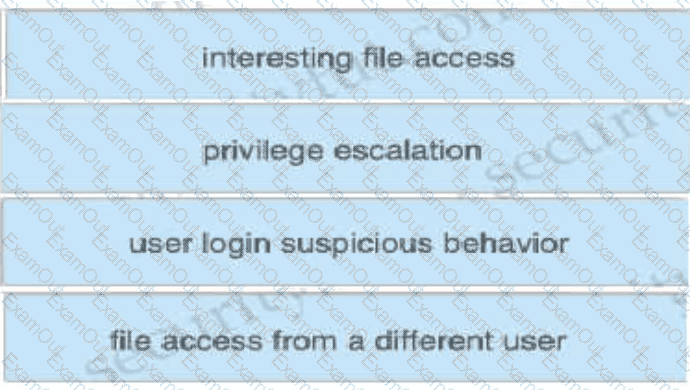
Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
What is a benefit of an endpoint patch management strategy?
Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?
Which two components do southbound APIs use to communicate with downstream devices? (Choose two.)
Which Cisco security solution protects remote users against phishing attacks when they are not connected to
the VPN?
Which solution is more secure than the traditional use of a username and password and encompasses at least two of the methods of authentication?
An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites but other sites are not accessible due to an error. Why is the error occurring?
An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?
