Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

Which two probes are configured to gather attributes of connected endpoints using Cisco Identity Services

Engine? (Choose two)

A.

RADIUS

B.

TACACS+

C.

DHCP

D.

sFlow

E.

SMTP

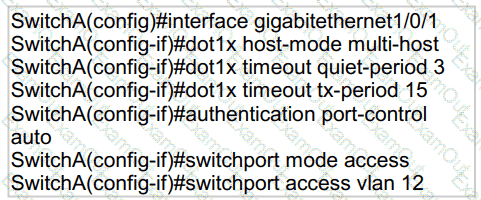
Refer to the exhibit.

question 137

An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?

A.

authentication open

B.

dotlx reauthentication

C.

cisp enable

D.

dot1x pae authenticator

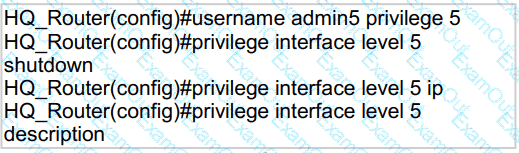
Refer to the exhibit.

question 138

A network administrator configures command authorization for the admin5 user. What is the admin5 user able to do on HQ_Router after this configuration?

A.

set the IP address of an interface

B.

complete no configurations

C.

complete all configurations

D.

add subinterfaces

What must be configured on Cisco Secure Endpoint to create a custom detection tile list to detect and quarantine future files?

A.

Use the simple custom detection feature and add each detection to the list.

B.

Add a network IP block allowed list to the configuration and add the blocked files.

C.

Create an advanced custom detection and upload the hash of each file

D.

Configure an application control allowed applications list to block the files

What is a characteristic of Dynamic ARP Inspection?

A.

DAI determines the validity of an ARP packet based on valid IP to MAC address bindings from the DHCPsnooping binding database.

B.

In a typical network, make all ports as trusted except for the ports connecting to switches, which areuntrusted

C.

DAI associates a trust state with each switch.

D.

DAI intercepts all ARP requests and responses on trusted ports only.

Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?

A.

RBAC

B.

ETHOS detection engine

C.

SPERO detection engine

D.

TETRA detection engine

What is a feature of Cisco NetFlow Secure Event Logging for Cisco ASAs?

A.

Multiple NetFlow collectors are supported

B.

Advanced NetFlow v9 templates and legacy v5 formatting are supported

C.

Secure NetFlow connections are optimized for Cisco Prime Infrastructure

D.

Flow-create events are delayed

Which two deployment modes does the Cisco ASA FirePower module support? (Choose two)

A.

transparent mode

B.

routed mode

C.

inline mode

D.

active mode

E.

passive monitor-only mode

Which two cryptographic algorithms are used with IPsec? (Choose two)

A.

AES-BAC

B.

AES-ABC

C.

HMAC-SHA1/SHA2

D.

Triple AMC-CBC

E.

AES-CBC

What is the difference between deceptive phishing and spear phishing?

A.

Deceptive phishing is an attacked aimed at a specific user in the organization who holds a C-level role.

B.

A spear phishing campaign is aimed at a specific person versus a group of people.

C.

Spear phishing is when the attack is aimed at the C-level executives of an organization.

D.

Deceptive phishing hijacks and manipulates the DNS server of the victim and redirects the user to a false webpage.

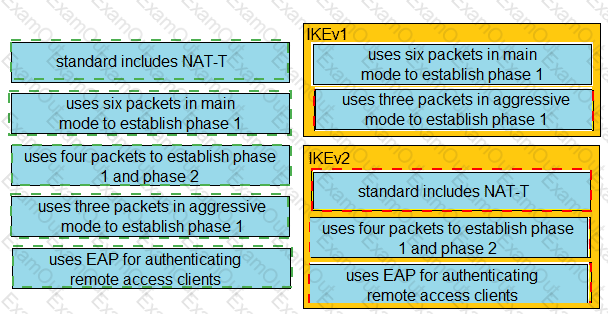
Drag and drop the descriptions from the left onto the correct protocol versions on the right.
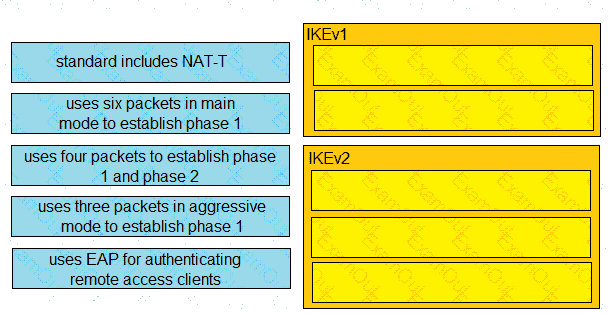
question 146

Why should organizations migrate to an MFA strategy for authentication?

A.

Single methods of authentication can be compromised more easily than MFA.

B.

Biometrics authentication leads to the need for MFA due to its ability to be hacked easily.

C.

MFA methods of authentication are never compromised.

D.

MFA does not require any piece of evidence for an authentication mechanism.

An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.

The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of

certificate should be presented to the end-user to accomplish this goal?

A.

third-party

B.

self-signed

C.

organization owned root

D.

SubCA

What must be enabled to secure SaaS-based applications?

A.

modular policy framework

B.

two-factor authentication

C.

application security gateway

D.

end-to-end encryption

What are two functions of IKEv1 but not IKEv2? (Choose two)

A.

NAT-T is supported in IKEv1 but rot in IKEv2.

B.

With IKEv1, when using aggressive mode, the initiator and responder identities are passed cleartext

C.

With IKEv1, mode negotiates faster than main mode

D.

IKEv1 uses EAP authentication

E.

IKEv1 conversations are initiated by the IKE_SA_INIT message