Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

What do tools like Jenkins, Octopus Deploy, and Azure DevOps provide in terms of application and

infrastructure automation?

A.

continuous integration and continuous deployment

B.

cloud application security broker

C.

compile-time instrumentation

D.

container orchestration

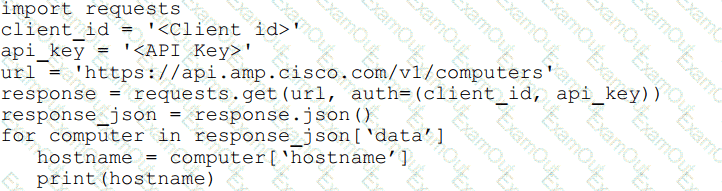
Refer to the exhibit.

question 92

What will happen when the Python script is executed?

A.

The hostname will be translated to an IP address and printed.

B.

The hostname will be printed for the client in the client ID field.

C.

The script will pull all computer hostnames and print them.

D.

The script will translate the IP address to FODN and print it

A company identified a phishing vulnerability during a pentest What are two ways the company can protect employees from the attack? (Choose two.)

A.

using Cisco Umbrella

B.

using Cisco ESA

C.

using Cisco FTD

D.

using an inline IPS/IDS in the network

E.

using Cisco ISE

Which factor must be considered when choosing the on-premise solution over the cloud-based one?

A.

With an on-premise solution, the provider is responsible for the installation and maintenance of the product, whereas with a cloud-based solution, the customer is responsible for it

B.

With a cloud-based solution, the provider is responsible for the installation, but the customer is responsible for the maintenance of the product.

C.

With an on-premise solution, the provider is responsible for the installation, but the customer is responsible for the maintenance of the product.

D.

With an on-premise solution, the customer is responsible for the installation and maintenance of theproduct, whereas with a cloud-based solution, the provider is responsible for it.

What is a benefit of using GET VPN over FlexVPN within a VPN deployment?

A.

GET VPN supports Remote Access VPNs

B.

GET VPN natively supports MPLS and private IP networks

C.

GET VPN uses multiple security associations for connections

D.

GET VPN interoperates with non-Cisco devices

In which two ways does Easy Connect help control network access when used with Cisco TrustSec? (Choose two)

A.

It allows multiple security products to share information and work together to enhance security posture in the network.

B.

It creates a dashboard in Cisco ISE that provides full visibility of all connected endpoints.

C.

It allows for the assignment of Security Group Tags and does not require 802.1x to be configured on the switch or the endpoint.

D.

It integrates with third-party products to provide better visibility throughout the network.

E.

It allows for managed endpoints that authenticate to AD to be mapped to Security Groups (PassiveID).

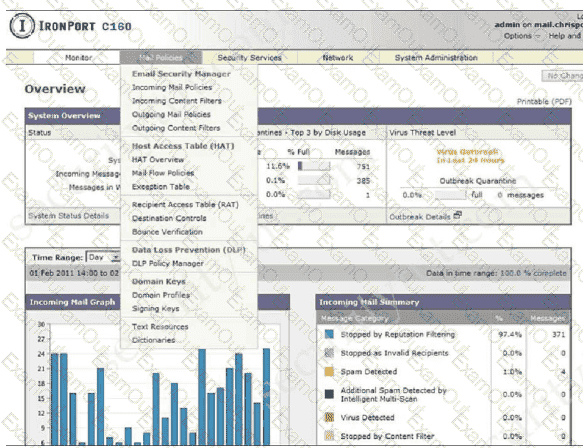
An organization received a large amount of SPAM messages over a short time period. In order to take action on the messages, it must be determined how harmful the messages are and this needs to happen dynamically.

What must be configured to accomplish this?
A.

Configure the Cisco WSA to modify policies based on the traffic seen

B.

Configure the Cisco ESA to receive real-time updates from Talos

C.

Configure the Cisco WSA to receive real-time updates from Talos

D.

Configure the Cisco ESA to modify policies based on the traffic seen

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

What is the process of performing automated static and dynamic analysis of files against preloaded

behavioral indicators for threat analysis?

A.

deep visibility scan

B.

point-in-time checks

C.

advanced sandboxing

D.

advanced scanning

Which two deployment model configurations are supported for Cisco FTDv in AWS? (Choose two)

A.

Cisco FTDv configured in routed mode and managed by an FMCv installed in AWS

B.

Cisco FTDv with one management interface and two traffic interfaces configured

C.

Cisco FTDv configured in routed mode and managed by a physical FMC appliance on premises

D.

Cisco FTDv with two management interfaces and one traffic interface configured

E.

Cisco FTDv configured in routed mode and IPv6 configured

Which threat involves software being used to gain unauthorized access to a computer system?

A.

virus

B.

NTP amplification

C.

ping of death

D.

HTTP flood

An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?

A.

Use DNSSEC between the endpoints and Cisco Umbrella DNS servers.

B.

Modify the Cisco Umbrella configuration to pass queries only to non-DNSSEC capable zones.

C.

Integrate Cisco Umbrella with Cisco CloudLock to ensure that DNSSEC is functional.

D.

Configure Cisco Umbrella and use DNSSEC for domain authentication to authoritative servers.

An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)

A.

Configure Cisco ACI to ingest AWS information.

B.

Configure Cisco Thousand Eyes to ingest AWS information.

C.

Send syslog from AWS to Cisco Stealthwatch Cloud.

D.

Send VPC Flow Logs to Cisco Stealthwatch Cloud.

E.

Configure Cisco Stealthwatch Cloud to ingest AWS information

Which open source tool does Cisco use to create graphical visualizations of network telemetry on Cisco IOS XE devices?

A.

InfluxDB

B.

Splunk

C.

SNMP

D.

Grafana

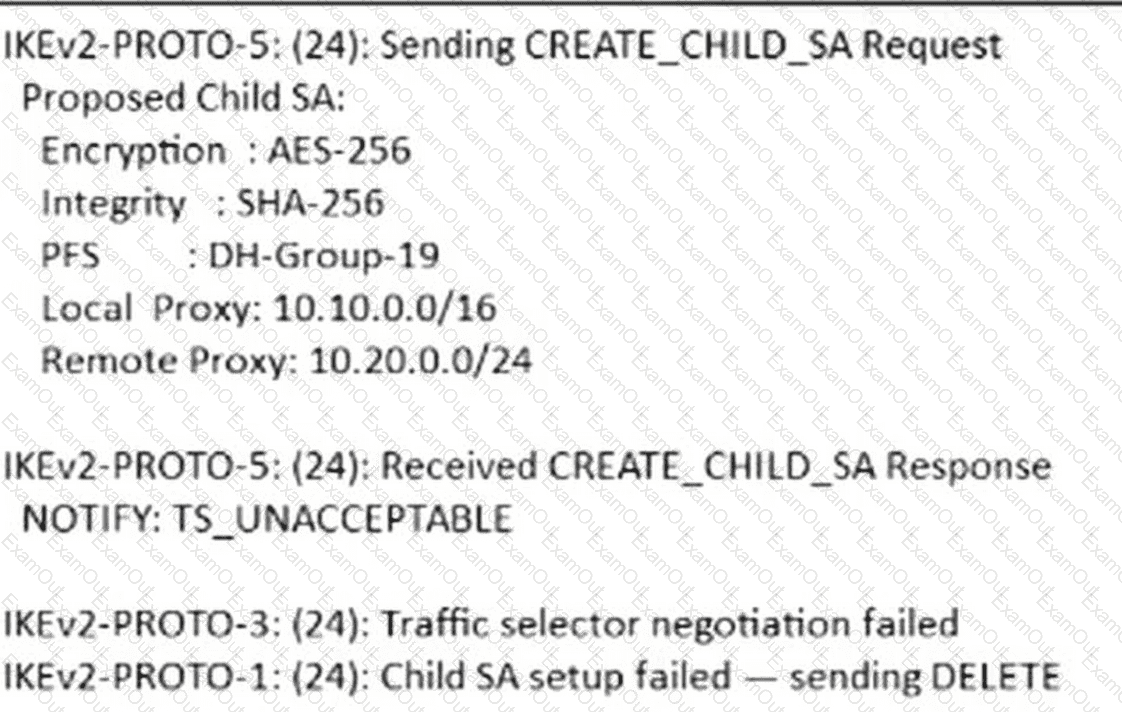
Refer to the exhibit.

question 105

A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_SA. The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?

A.

Align the protected network definitions on both firewalls so that the local and remote traffic selectors proposed during CREATE_CHILD_SA match on both peers.

B.

Change the IPsec encryption algorithm from AES-256 to AES-128 on the initiating firewall and redeploy the VPN policy.

C.

Extend the IKE SA lifetime on both firewalls to give CREATE_CHILD_SA sufficient time to complete the negotiation before the Phase 1 SA expires.

D.

Remove DH Group 19 from the IPsec proposal on the initiating FTD because the TS_UNACCEPTABLE notification indicates that the responder does not support the proposed PFS group.