
Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?
Which two capabilities does TAXII support? (Choose two)
An administrator has been tasked with configuring the Cisco Secure Email Gateway to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two.)
Which problem Is solved by deploying a multicontext firewall?
Which attack gives unauthorized access to files on the web server?
Refer to the exhibit.
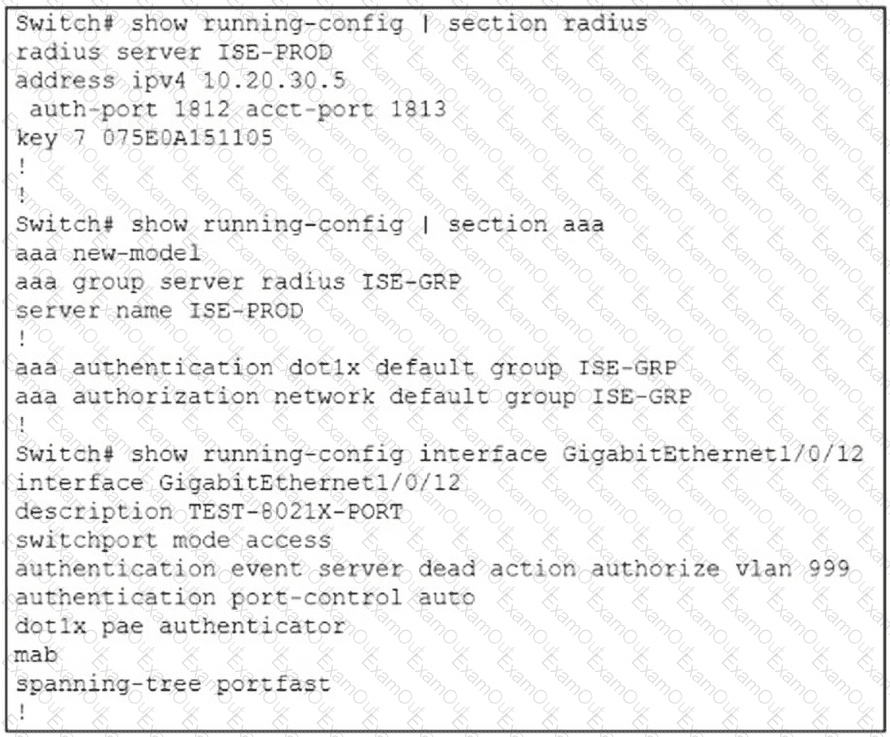
A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown” and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?
Which two authentication protocols are supported by the Cisco WSA? (Choose two.)
What provides the ability to program and monitor networks from somewhere other than the DNAC GUI?
Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?
In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)
Where are individual sites specified to be blacklisted in Cisco Umbrella?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
A Cisco AMP for Endpoints administrator configures a custom detection policy to add specific MD5 signatures The configuration is created in the simple detection policy section, but it does not work What is the reason for this failure?
An email administrator is setting up a new Cisco ESA. The administrator wants to enable the blocking of greymail for the end user. Which feature must the administrator enable first?
What is a characteristic of an EDR solution and not of an EPP solution?
