Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

A network administrator needs a solution to match traffic and allow or deny the traffic based on the type of application, not just the source or destination address and port used. Which kind of security product must the network administrator implement to meet this requirement?

A.

Next-generation Intrusion Prevention System

B.

Next-generation Firewall

C.

Web Application Firewall

D.

Intrusion Detection System

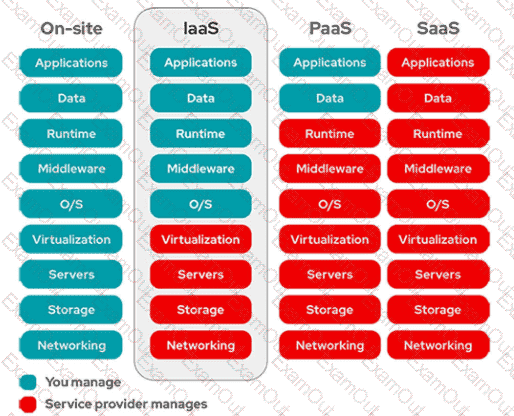
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)
A.

virtualization

B.

middleware

C.

operating systems

D.

applications

E.

data

What is a functional difference between Cisco AMP for Endpoints and Cisco Umbrella Roaming Client?

A.

The Umbrella Roaming client stops and tracks malicious activity on hosts, and AMP for Endpoints tracks only URL-based threats.

B.

The Umbrella Roaming Client authenticates users and provides segmentation, and AMP for Endpoints allows only for VPN connectivity

C.

AMP for Endpoints authenticates users and provides segmentation, and the Umbrella Roaming Client allows only for VPN connectivity.

D.

AMP for Endpoints stops and tracks malicious activity on hosts, and the Umbrella Roaming Client tracks only URL-based threats.

A large organization wants to deploy a security appliance in the public cloud to form a site-to-site VPN

and link the public cloud environment to the private cloud in the headquarters data center. Which Cisco

security appliance meets these requirements?

A.

Cisco Cloud Orchestrator

B.

Cisco ASAV

C.

Cisco WSAV

D.

Cisco Stealthwatch Cloud

An engineer is configuring Cisco Secure Endpoint to enhance network security by specifying a large set of external IP addresses that must be monitored for potential threats. The engineer is configuring an IP List and must add the IP addresses to the list. Which configuration action must the engineer take next to meet the requirement?

A.

Add the IP addresses using the global bulk configuration wizard.

B.

Automate a threat-feed subscription using an API.

C.

Use the data-upload function and import a file formatted as JSON.

D.

Use the Add Multiple Rows feature and paste all addresses into the input field.

In a PaaS model, which layer is the tenant responsible for maintaining and patching?

A.

hypervisor

B.

virtual machine

C.

network

D.

application

What are two advantages of using Cisco Any connect over DMVPN? (Choose two)

A.

It provides spoke-to-spoke communications without traversing the hub

B.

It allows different routing protocols to work over the tunnel

C.

It allows customization of access policies based on user identity

D.

It allows multiple sites to connect to the data center

E.

It enables VPN access for individual users from their machines

Which component of Cisco umbrella architecture increases reliability of the service?

A.

Anycast IP

B.

AMP Threat grid

C.

Cisco Talos

D.

BGP route reflector

Which two fields are defined in the NetFlow flow? (Choose two)

A.

type of service byte

B.

class of service bits

C.

Layer 4 protocol type

D.

destination port

E.

output logical interface

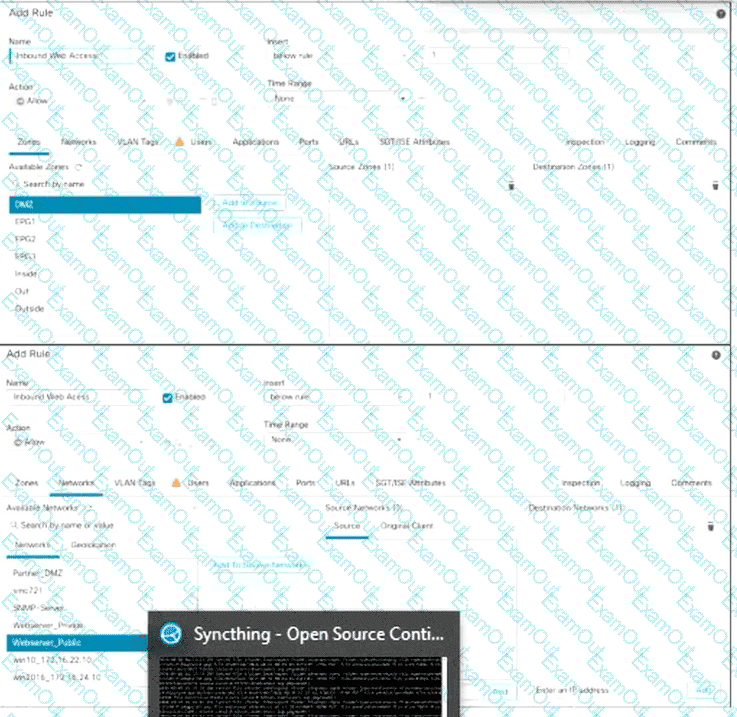
Refer to the exhibit.

question 25

A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)

A.

Add DMZ as the Source Zone and Outside as the Destination Zone.

B.

Add Webserver_Private as the Source Network and Webserver_Public as the Destination Network.

C.

Add Any as the Source Network and Webserver_Private as the Destination Network.

D.

Add Any as the Source Network and Webserver_Public as the Destination Network.

E.

Add Outside as the Source Zone and DMZ as the Destination Zone.

An organization wants to use Cisco FTD or Cisco ASA devices. Specific URLs must be blocked from being

accessed via the firewall which requires that the administrator input the bad URL categories that the

organization wants blocked into the access policy. Which solution should be used to meet this requirement?

A.

Cisco ASA because it enables URL filtering and blocks malicious URLs by default, whereas Cisco FTDdoes not

B.

Cisco ASA because it includes URL filtering in the access control policy capabilities, whereas Cisco FTD does not

C.

Cisco FTD because it includes URL filtering in the access control policy capabilities, whereas Cisco ASA does not

D.

Cisco FTD because it enables URL filtering and blocks malicious URLs by default, whereas Cisco ASA does not

A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?

A.

EDR

B.

CASB

C.

Secure Firewall

D.

CWPP

Which statement describes a traffic profile on a Cisco Next Generation Intrusion Prevention System?

A.

It allows traffic if it does not meet the profile.

B.

It defines a traffic baseline for traffic anomaly deduction.

C.

It inspects hosts that meet the profile with more intrusion rules.

D.

It blocks traffic if it does not meet the profile.

What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?

A.

It allows the administrator to quarantine malicious files so that the application can function, just notmaliciously.

B.

It discovers and controls cloud apps that are connected to a company’s corporate environment.

C.

It deletes any application that does not belong in the network.

D.

It sends the application information to an administrator to act on.

What is the most common type of data exfiltration that organizations currently experience?

A.

HTTPS file upload site

B.

Microsoft Windows network shares

C.

SQL database injections

D.

encrypted SMTP