
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

An organization is trying to implement micro-segmentation on the network and wants to be able to gain visibility on the applications within the network. The solution must be able to maintain and force compliance. Which product should be used to meet these requirements?

A.

Cisco Umbrella

B.

Cisco AMP

C.

Cisco Stealthwatch

D.

Cisco Tetration

An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed

through the Cisco Umbrella network. Which action tests the routing?

A.

Ensure that the client computers are pointing to the on-premises DNS servers.

B.

Enable the Intelligent Proxy to validate that traffic is being routed correctly.

C.

Add the public IP address that the client computers are behind to a Core Identity.

D.

Browse to http://welcome.umbrella.com/ to validate that the new identity is working.

A recent change left network engineers unable to SSH into a branch Cisco Catalyst switch. The engineer confirms that the TACACS server group TACACS-GROUP is defined but unreachable. There is no fallback to the local database when TACACS+ is unavailable. Security policy requires TACACS+ as the primary authentication method with automatic fallback to local accounts. Which configuration command must be added to resolve the issue?

A.

aaa authentication login ssh LOCAL TACACS-GROUP

B.

aaa authentication login group TACACS-GROUP local

C.

aaa authentication login default group TACACS-GROUP local

D.

aaa authentication serial console TACACS-GROUP LOCAL

What is the concept of Cl/CD pipelining?

A.

The project is split into several phases where one phase cannot start before the previous phase finishes successfully.

B.

The project code is centrally maintained and each code change should trigger an automated build and test sequence

C.

The project is split into time-limited cycles and focuses on pair programming for continuous code review

D.

Each project phase is independent from other phases to maintain adaptiveness and continual improvement

What is a key feature of the Bring Your Own Device (BYOD) capability in Cisco ISE?

A.

Provide temporary Internet access for the personal devices of guest users.

B.

Assess the security posture of personal devices before network access is allowed.

C.

Fully manage network devices based on their characteristics before access is allowed.

D.

Encrypt endpoint data according to predefined security policies.

An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which

vulnerability allows the attacker to see the passwords being transmitted in clear text?

A.

weak passwords for authentication

B.

unencrypted links for traffic

C.

software bugs on applications

D.

improper file security

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

A.

Create an LDAP authentication realm and disable transparent user identification.

B.

Create NTLM or Kerberos authentication realm and enable transparent user identification.

C.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

D.

The eDirectory client must be installed on each client workstation.

E.

Deploy a separate eDirectory server; the dent IP address is recorded in this server.

A network engineer has configured a NTP server on a Cisco ASA. The Cisco ASA has IP reachability to the

NTP server and is not filtering any traffic. The show ntp association detail command indicates that the

configured NTP server is unsynchronized and has a stratum of 16. What is the cause of this issue?

A.

Resynchronization of NTP is not forced

B.

NTP is not configured to use a working server.

C.

An access list entry for UDP port 123 on the inside interface is missing.

D.

An access list entry for UDP port 123 on the outside interface is missing.

What is a function of the Layer 4 Traffic Monitor on a Cisco WSA?

A.

blocks traffic from URL categories that are known to contain malicious content

B.

decrypts SSL traffic to monitor for malicious content

C.

monitors suspicious traffic across all the TCP/UDP ports

D.

prevents data exfiltration by searching all the network traffic for specified sensitive information

What is the most commonly used protocol for network telemetry?

A.

SMTP

B.

SNMP

C.

TFTP

D.

NctFlow

An engineer is configuring Dropbox integration with Cisco Cloudlock. Which action must be taken before granting API access in the Dropbox admin console?

A.

Authorize Dropbox within the Platform settings in the Cisco Cloudlock portal.

B.

Add Dropbox to the Cisco Cloudlock Authentication and API section in the Cisco Cloudlock portal.

C.

Send an API request to Cisco Cloudlock from Dropbox admin portal.

D.

Add Cisco Cloudlock to the Dropbox admin portal.

What is the primary role of the Cisco Email Security Appliance?
A.

Mail Submission Agent

B.

Mail Transfer Agent

C.

Mail Delivery Agent

D.

Mail User Agent

question 238

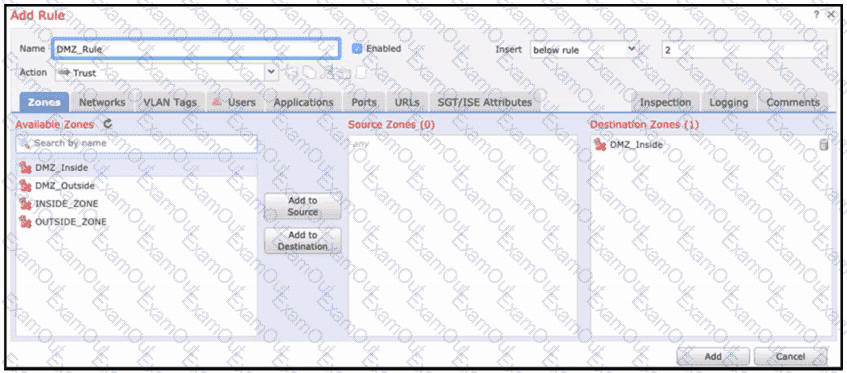
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?

A.

All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.

B.

No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.

C.

No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.

D.

All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.

Which technology provides a combination of endpoint protection endpoint detection, and response?
A.

Cisco AMP

B.

Cisco Talos

C.

Cisco Threat Grid

D.

Cisco Umbrella

question 240

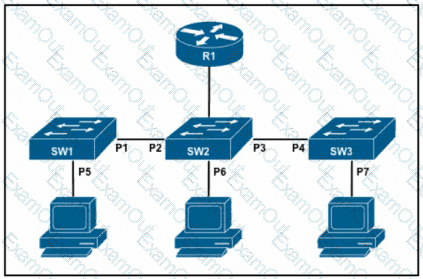
Refer to the exhibit. The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

A.

P2 and P3 only

B.

P2, P3, and P6 only

C.

P5, P6, and P7 only

D.

P1, P2, P3, and P4 only