Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

A security engineer must add destinations into a destination list in Cisco Umbrella. What describes the application of these changes?

A.

The changes are applied immediately it the destination list is part or a policy.

B.

The destination list must be removed from the policy before changes are made to It.

C.

The changes are applied only after the configuration is saved in Cisco Umbrella.

D.

The user role of Block Page Bypass or higher is needed to perform these changes.

Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?

A.

Performing static routing configuration checks

B.

Conducting software composition analysis during builds

C.

Using dynamic routing between Kubernetes clusters

D.

Setting up round-robin DNS resolution for service discovery

In which scenario is endpoint-based security the solution?

A.

inspecting encrypted traffic

B.

device profiling and authorization

C.

performing signature-based application control

D.

inspecting a password-protected archive

Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?

A.

GET VPN

B.

IPsec DVTI

C.

DMVPN

D.

FlexVPN

Which information is required when adding a device to Firepower Management Center?

A.

username and password

B.

encryption method

C.

device serial number

D.

registration key

Drag and drop the common security threats from the left onto the definitions on the right.
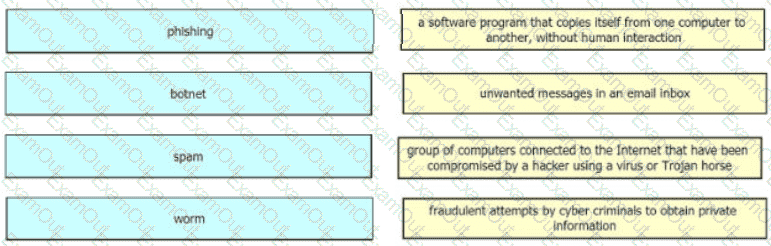
question 201

What is the process In DevSecOps where all changes In the central code repository are merged and synchronized?

A.

CD

B.

EP

C.

CI

D.

QA

Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?

A.

Cisco Advanced Malware Protection

B.

Cisco Stealthwatch

C.

Cisco Identity Services Engine

D.

Cisco AnyConnect

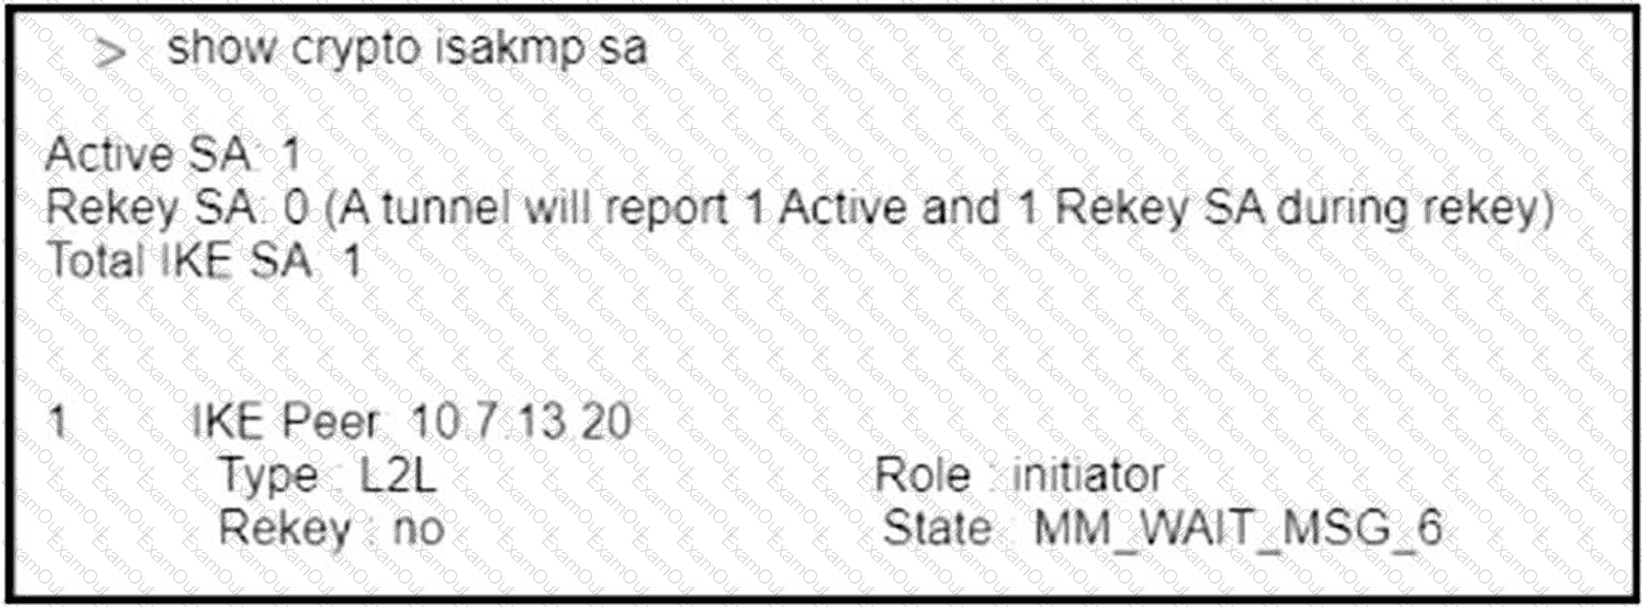
Refer to the exhibit.

question 204

During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?

A.

Configure matching peer-identity values under each tunnel group on both endpoints.

B.

Add the same pre-shared key on both peers within their tunnel-group attributes.

C.

Implement identical Diffie-Hellman group numbers within the active IKEv1 policy.

D.

Apply equivalent transform sets and lifetimes inside the crypto-map entries.

Which type of algorithm provides the highest level of protection against brute-force attacks?

A.

PFS

B.

HMAC

C.

MD5

D.

SHA

What provides visibility and awareness into what is currently occurring on the network?

A.

CMX

B.

WMI

C.

Prime Infrastructure

D.

Telemetry

A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?

A.

denial -of-service

B.

cross-site request forgery

C.

man-in-the-middle

D.

SQL injection

Which VPN provides scalability for organizations with many remote sites?

A.

DMVPN

B.

site-to-site iPsec

C.

SSL VPN

D.

GRE over IPsec

What are two facts about WSA HTTP proxy configuration with a PAC file? (Choose two.)

A.

It is defined as a Transparent proxy deployment.

B.

In a dual-NIC configuration, the PAC file directs traffic through the two NICs to the proxy.

C.

The PAC file, which references the proxy, is deployed to the client web browser.

D.

It is defined as an Explicit proxy deployment.

E.

It is defined as a Bridge proxy deployment.

Which command is used to log all events to a destination colector 209.165.201.107?

A.

CiscoASA(config-pmap-c)#flow-export event-type flow-update destination 209.165.201.10

B.

CiscoASA(config-cmap)# flow-export event-type all destination 209.165.201.

C.

CiscoASA(config-pmap-c)#flow-export event-type all destination 209.165.201.10

D.

CiscoASA(config-cmap)#flow-export event-type flow-update destination 209.165.201.10