
The security architect has concluded that the optimal mail flow positions the existing Cisco Secure Email Gateways as the first termination point for inbound messages, while Cisco Secure Email Threat Defense is positioned between the Secure Email Gateways and the cloud mail platform. The security engineer has been asked to configure the incoming-traffic domain setting in Cisco Secure Email Threat Defense so that it reflects the Secure Email Gateway handling inbound messages ahead of the service. Which domain configuration for incoming traffic must be selected to meet the requirement?
Which Cisco solution extends network visibility, threat detection, and analytics to public cloud environments?
Refer to the exhibit.
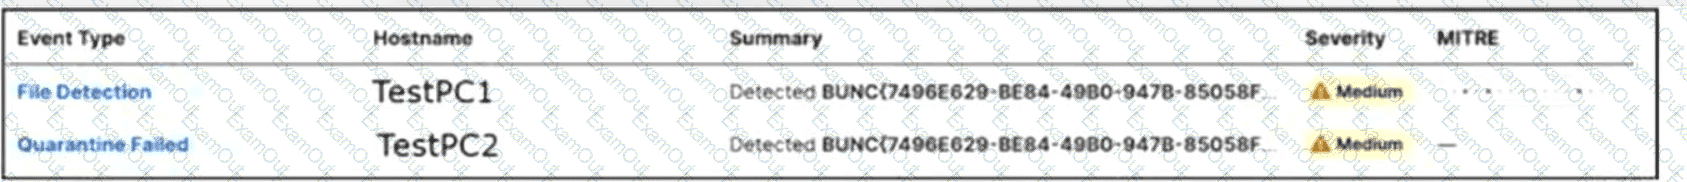
A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network
is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?
An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively used by devices, using many of the default policy elements.
What else must be done to accomplish this task?
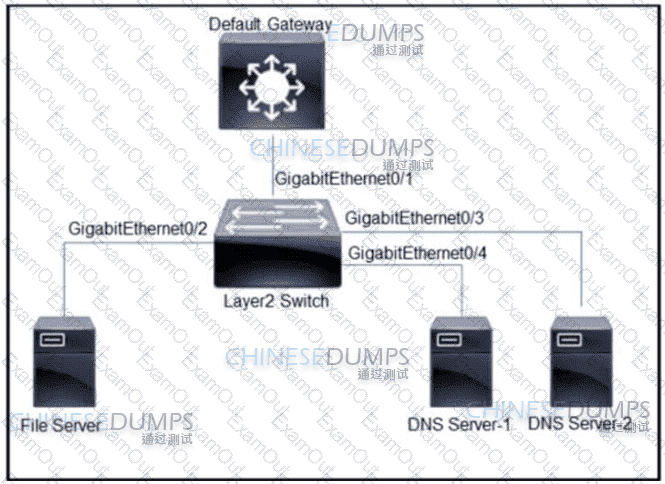
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?
A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.
How does the switch behave in this situation?
What is the difference between deceptive phishing and spear phishing?
What is the purpose of the Decrypt for Application Detection feature within the WSA Decryption options?
Which Cisco AMP feature allows an engineer to look back to trace past activities, such as file and process activity on an endpoint?
An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:
• Governance with role-based access control based on the principle of least privilege
• TLS 1.3 with signed certificates
• AES-256 with MD5
What must be configured to complete the secure implementation?
What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an
organization? (Choose two)
What is an advantage of network telemetry over SNMP pulls?
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
What features does Cisco FTDv provide over ASAv?
