
Refer to the exhibit.
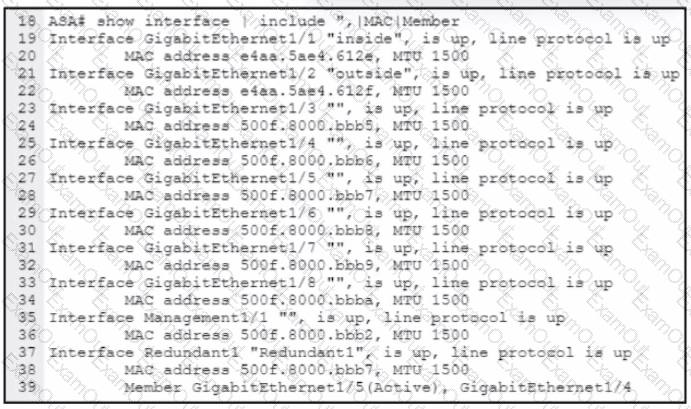
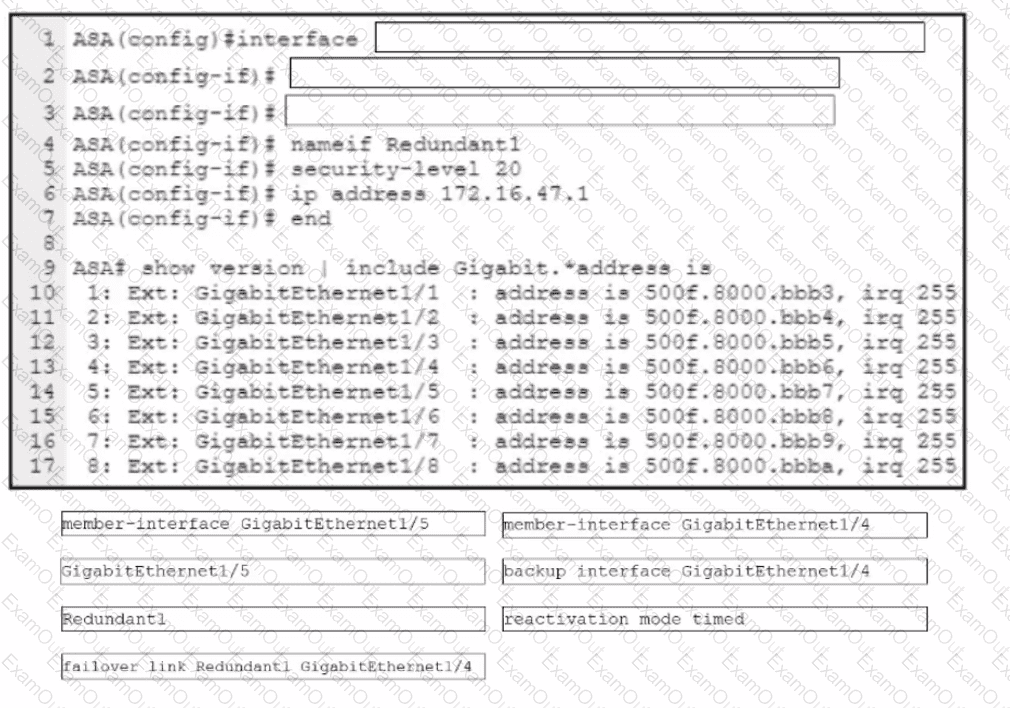
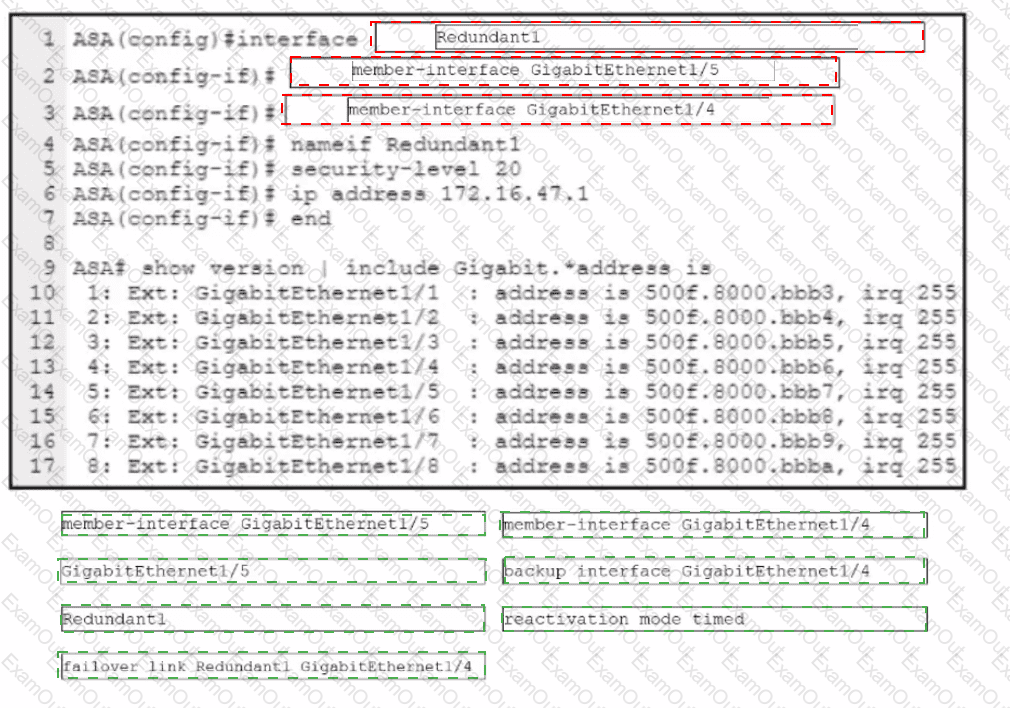
An engineer must configure a connection on a Cisco Secure Firewall running ASA to ensure that the secondary interface takes over all the functions of the primary interface if the primary interface fails. Drag and drop the code snippets from the bottom onto the boxes in the CLI commands to configure the failover. Not all options are used.
An administrator is attempting to remotely log into a switch in the data centre using SSH and is unable to connect. How does the administrator confirm that traffic is reaching the firewall?
When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?
A network security engineer must replace a faulty Cisco FTD device in a high availability pair. Which action must be taken while replacing the faulty unit?
Refer to the exhibit.
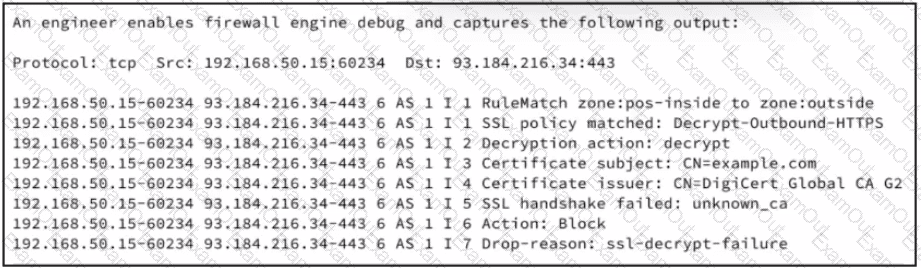
Security engineer is investigating an issue where outbound HTTPS traffic from an endpoint using network 192.168.50.0/24 is being blocked. The Cisco Secure Firewall Threat Defense is configured with a TLS decryption policy applied to all outbound web traffic. An engineer enables firewall engine debug and captures the output. Which action must be performed to resolve the issue?
What is the role of realms in the Cisco ISE and Cisco FMC integration?
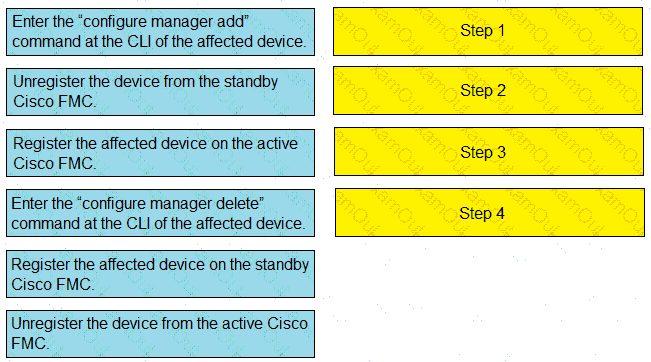
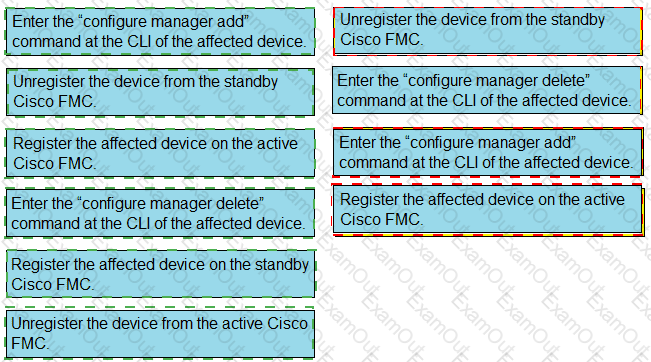
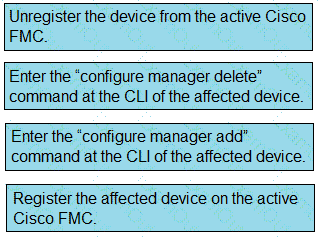
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
An engineer is configuring URL filtering tor a Cisco Secure Firewall Threat Defense device in Cisco Secure Firewall Management Centre. Use ' s must receive a warning when they access
..wwww badaduitsito com with the option of continuing to the website if they choose to No other websites should he blocked. Which two actions must the engineer take to moot these requirements?
What is the difference between inline and inline tap on Cisco Firepower?
An engineer is configuring two new Cisco Secure Firewall Threat Defense devices to replace the existing firewalls. Network traffic must be analyzed for intrusion events without impacting the traffic. What must the engineer implement next to accomplish the goal?
