
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

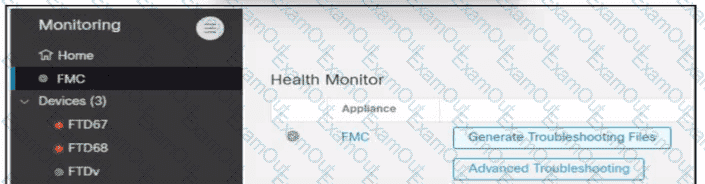
Refer to the exhibit.
question 21

An engineer generates troubleshooting files in Cisco Secure Firewall Management Center (FMC). A successfully completed task Is removed before the files are downloaded. Which two actions must be taken to determine the filename and obtain the generated troubleshooting files without regenerating them? (Choose two.)

A.

Use an FTP client Hi expert mode on Secure FMC lo upload the files to the FTP server.

B.

Go to the same screen as shown in the exhibit, click Advanced Troubleshooting, enter the rile name, and then start the download

C.

Connect to CU on the FTD67 and FTD66 devices and copy the tiles from flash to the PIP server.

D.

Go to expert mode on Secure FMC. list the contents of/Var/common, and determine the correct filename from the output

E.

Click System Monitoring, men Audit to determine the correct filename from the line containing the Generate Troubleshooting Files string.

While integrating Cisco Umbrella with Cisco Threat Response, a network security engineer wants to automatically push blocking of domains from the Cisco Threat Response interface to Cisco Umbrella. Which API meets this requirement?
A.

investigate

B.

reporting

C.

enforcement

D.

REST

question 23

question 23

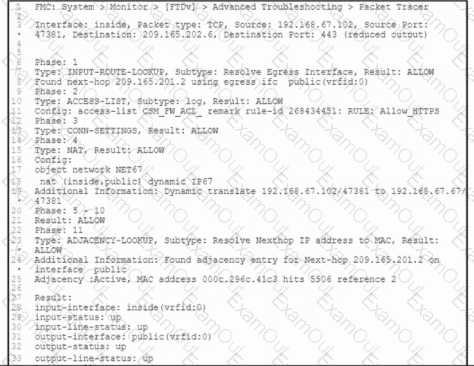
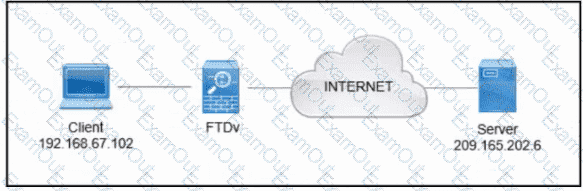
Refer to the exhibit. A client that has IP address 192.168.67.102 reports issues when connecting to a remote server. Based on the topology and output of packet tracer tool, which action resolves the connectivity issue?

A.

Add the route to the destination.

B.

Unblock the access rule on FTDv.

C.

Restart the client-side application.

D.

Reconfigure NAT on FTDv.

When deploying a Cisco ASA Firepower module, an organization wants to evaluate the contents of the traffic without affecting the network. It is currently configured to have more than one instance of the same device on the physical appliance Which deployment mode meets the needs of the organization?

A.

inline tap monitor-only mode

B.

passive monitor-only mode

C.

passive tap monitor-only mode

D.

inline mode

An engineer is using the configure manager add < FMC IP > Cisc402098527 command to add a new Cisco FTD device to the Cisco FMC; however, the device is not being added. Why Is this occurring?

A.

The NAT ID is required since the Cisco FMC is behind a NAT device.

B.

The IP address used should be that of the Cisco FTD. not the Cisco FMC.

C.

DONOTRESOLVE must be added to the command

D.

The registration key is missing from the command

A network administrator wants to configure a Cisco Secure Firewall Threat Defense instance managed by Cisco Secure Firewall Management Center to block traffic to known cryptomning networks. Which system settings must the administrator configure in Secure Firewall Management Center to meet the requirement?

A.

Access Policy. Security Intelligence

B.

Malware Policy.

C.

Rules Intrusion Policy. Security Intelligence

D.

Access Policy. Rules

Which action should you take when Cisco Threat Response notifies you that AMP has identified a file as malware?

A.

Add the malicious file to the block list.

B.

Send a snapshot to Cisco for technical support.

C.

Forward the result of the investigation to an external threat-analysis engine.

D.

Wait for Cisco Threat Response to automatically block the malware.

A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?

A.

The destination MAC address is optional if a VLAN ID value is entered

B.

Only the UDP packet type is supported

C.

The output format option for the packet logs unavailable

D.

The VLAN ID and destination MAC address are optional

What is a benefit of implementing Integrated Routing and Bridging (IRB) on a Cisco Secure Firewall device?

A.

Multiple physical interfaces on the device can be on the same VLAN.

B.

Uptime is increased by preventing the device from being a single point of failure.

C.

Customers with different security policies can reside on the same device.

D.

Threat information can be dynamically updated from Cisco Talos.

An engineer is reviewing an existing custom server fingerprint on a Cisco Secure Firewall because the current information is inaccurate. Which action must the engineer take to improve the accuracy of the network discovery rules?

A.

Exclude the IP address that is used to communicate with the monitored host.

B.

Exclude the ports that must be skipped.

C.

Add NetFlow monitoring for the network segment.

D.

Set one common rule to override the reports in the multidomain environment.