
A customer follows the Zero Trust model and explicitly verifies each attempt to access its corporate applications.
The customer discovers that several endpoints are infected with malware.
The customer suspends access attempts from the infected endpoints.
The malware is removed from the end point.
Which two conditions must be met before endpoint users can access the corporate applications again? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains multiple network security groups (NSGs), multiple virtual machines, and an Azure Bastion host named bastion1.
Several NSGs contain rules that allow direct RDP access to the virtual machines by bypassing bastion!
You need to ensure that the virtual machines can be accessed only by using bastion! The solution must prevent the use of NSG rules to bypass bastion1.
What should you include in the solution?
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.
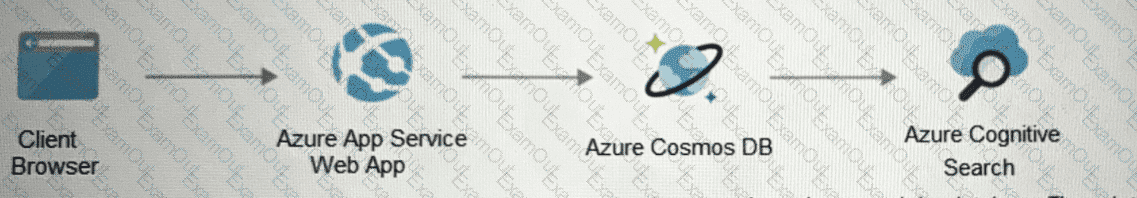
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend creating private endpoints for the web app and the database layer.
Does this meet the goal?
You have an Azure subscription that contains a Microsoft Sentinel workspace.
Your on-premises network contains firewalls that support forwarding event logs m the Common Event Format (CEF). There is no built-in Microsoft Sentinel connector for the firewalls
You need to recommend a solution to ingest events from the firewalls into Microsoft Sentinel.
What should you include m the recommendation?
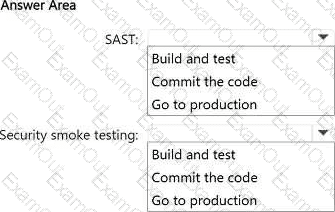
You have an Azure subscription that contains multiple apps. The apps are deployed by using continuous integration and continuous delivery (CI/CD) pipelines in Azure DevOps.
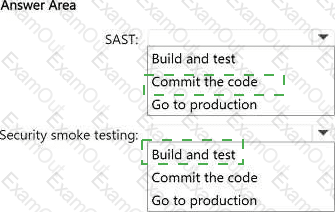
You need to integrate static application security testing (SAST) and security smoke testing into the pipelines based on Microsoft Cloud Adoption Framework for Azure principles.
At which stage of the CI/CID process should each type of test be integrated? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You are designing a new Azure environment based on the security best practices of the Microsoft Cloud Adoption Framework for Azure. The environment will contain one subscription for shared infrastructure components and three separate subscriptions for applications.
You need to recommend a deployment solution that includes network security groups (NSGs) Azure Key Vault, and Azure Bastion. The solution must minimize deployment effort and follow security best practices of the Microsoft Cloud Adoption Framework for Azure.
What should you include in the recommendation?
You are designing new Azure applications based on security best practices from the Microsoft Cloud Adoption Framework for Azure .
Each application will be deployed to a dedicated and secure environment that will contain isolated instances of the following key Azure security resources:
• Azure Key Vault
• Virtual networks
• An Azure subscription
• Azure Policy assignments
• Network security groups (NSGs)
• Role-based access control (RBAC) assignments
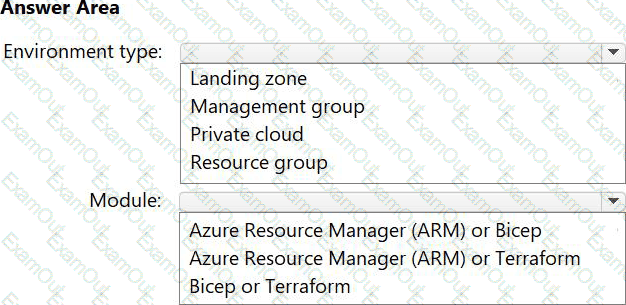
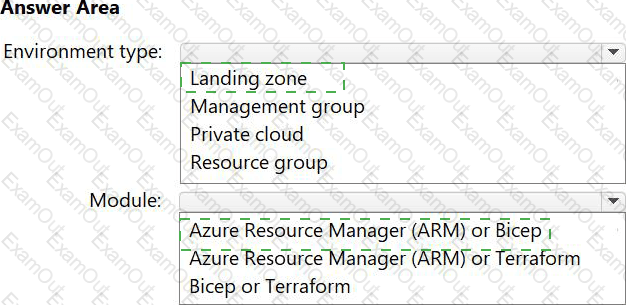
You need to recommend which type of environment and which module to use to deploy the applications. The solution must use infrastructure as code (IaC) to deploy each application environment.
What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that contains a group named Group!. The subscription is linked to a Microsoft Entra ID P1 tenant.
You have an external software as a service (SaaS) application named Appl. App1 is managed by using a web-based admin portal and supports the use of Microsoft Entra credentials.
You need to ensure that only the members of Group1 who sign in from Microsoft Entra joined devices can access the admin portal of App1
What should you create first in Microsoft Entra?
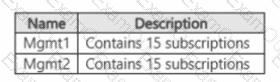
You have a Microsoft Entra tenant named contoso.com. You have 30 Azure subscriptions that are linked to contoso.com. The tenant contains the management groups shown in the following table.
You need to design a governance solution to manage access to all the Azure Storage accounts across the subscriptions. The solution must meet the following requirements:
• Use custom role-based access control (RBAQ to provide granular access to control plane and data plane operations.
• Minimize administrative effort.
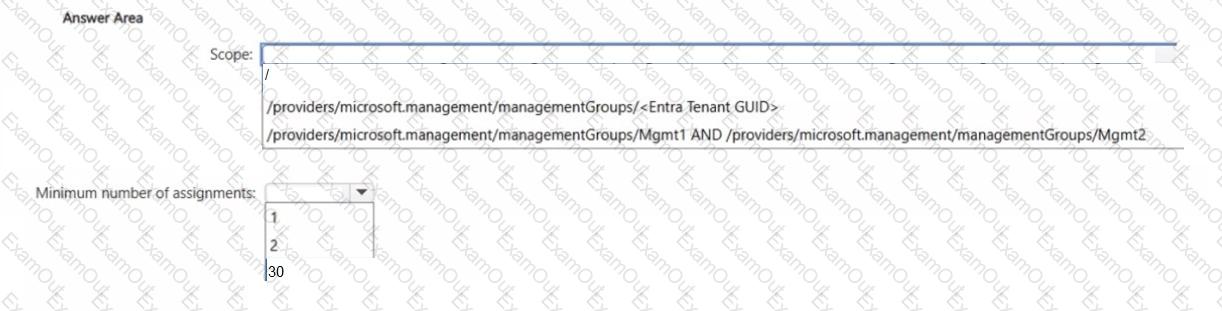
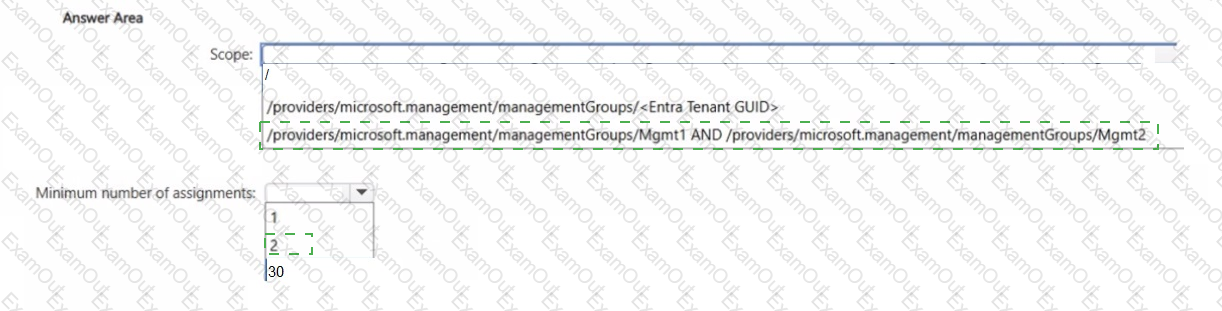
At which scope should you assign the roles, and what is the minimum number of assignments per role? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 tenant named contoso.com.
You need to ensure that users can authenticate only to contoso.com. The solution must meet the following requirements:
• Prevent the users from authenticating to other Microsoft 365 tenants.
• Minimize administrative effort.
What should you use?
