
You use Azure Pipelines with Azure Repos to implement continuous integration and continuous deployment (O/CD) workflows for the deployment of applications to Azure. You need to recommend what to include in dynamic application security testing (DAST) based on the principles of the Microsoft Cloud Adoption Framework for Azure. What should you recommend?
You have two on-premises servers named Server! and Server2 that run Windows Server. Server1 contains an app named App1 and is isolated from the internet.
You have a Microsoft Entra tenant
You plan to deploy Global Secure Access to provide remote access to App1.
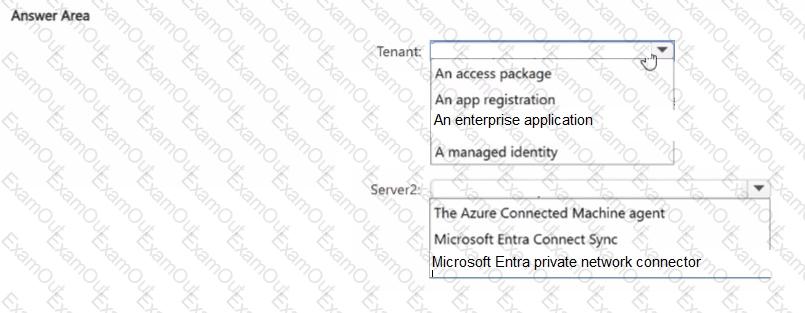
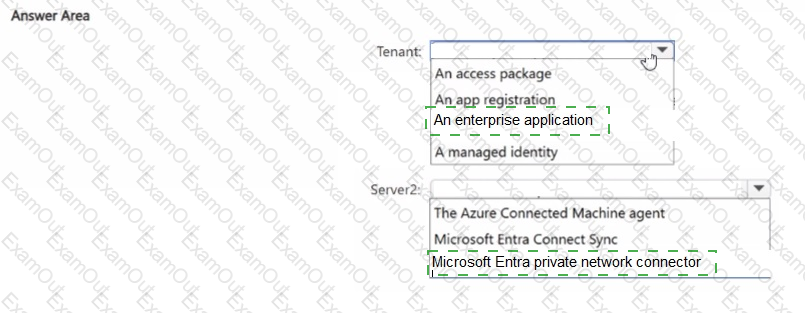
You need to configure the tenant and Server2 to support the planned deployment. The solution must ensure that when users attempt to access App1, they must authenticate by using their Microsoft Entra credentials.
What should you create in the tenant, and what should you install on Server2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your network contains an Active Directory Domain Services (AD DS) domain named Domain1.
You have a Microsoft Entra tenant.
Domain1 syncs with the tenant by using Microsoft Entra Connect.
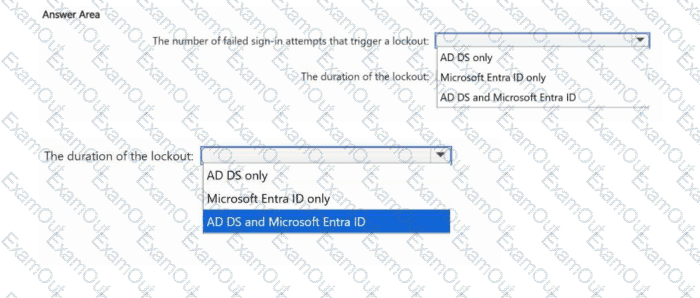
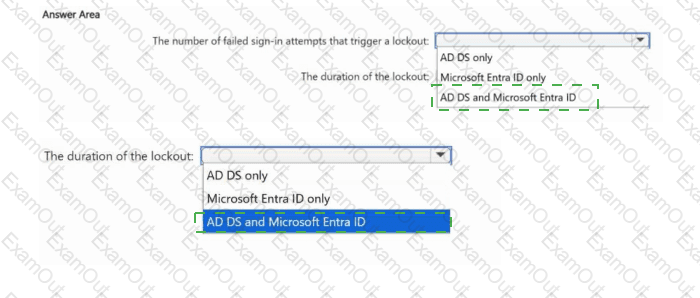
You need to evaluate Microsoft Entra smart lockout by testing the following account lockout considerations:
The number of failed sign-in attempts that trigger a lockout.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.
You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend enabling the VM Access extension on all virtual machines.
Does this meet the goal?
You have a hybrid cloud infrastructure.
You plan to deploy the Azure applications shown in the following table.
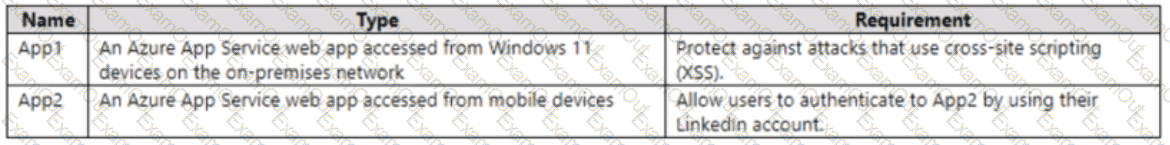
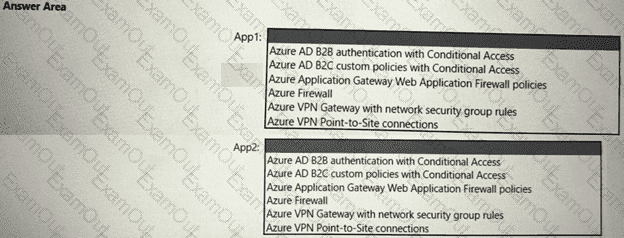
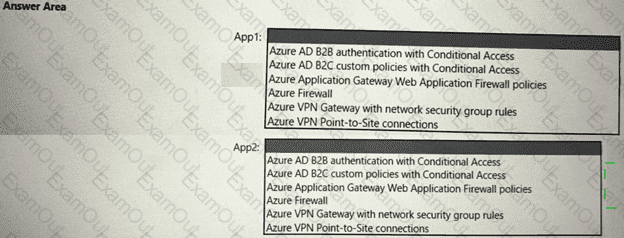
What should you use to meet the requirement of each app? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 E5 subscription.
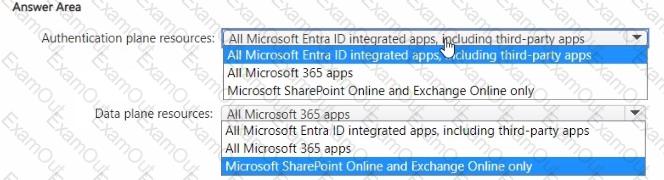
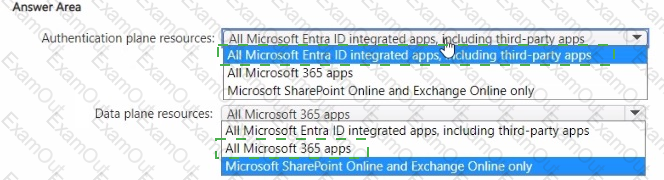
You plan to deploy Global Secure Access universal tenant restrictions v2.
Which authentication plane resources and which data plane resources will be protected? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to recommend a strategy for routing internet-bound traffic from the landing zones. The solution must meet the landing zone requirements.
What should you recommend as part of the landing zone deployment?
You have a hybrid Azure AD tenant that has pass-through authentication enabled.
You are designing an identity security strategy.
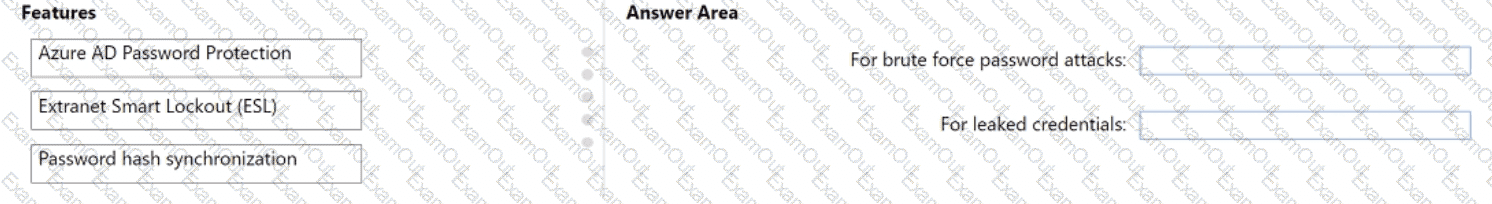
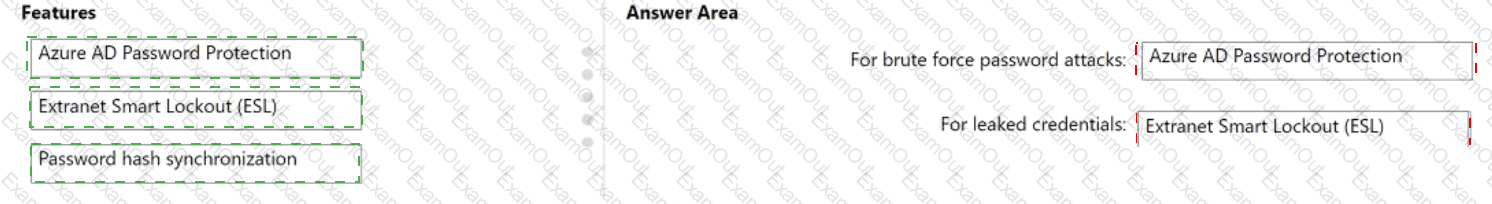
You need to minimize the impact of brute force password attacks and leaked credentials of hybrid identities.
What should you include in the design? To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
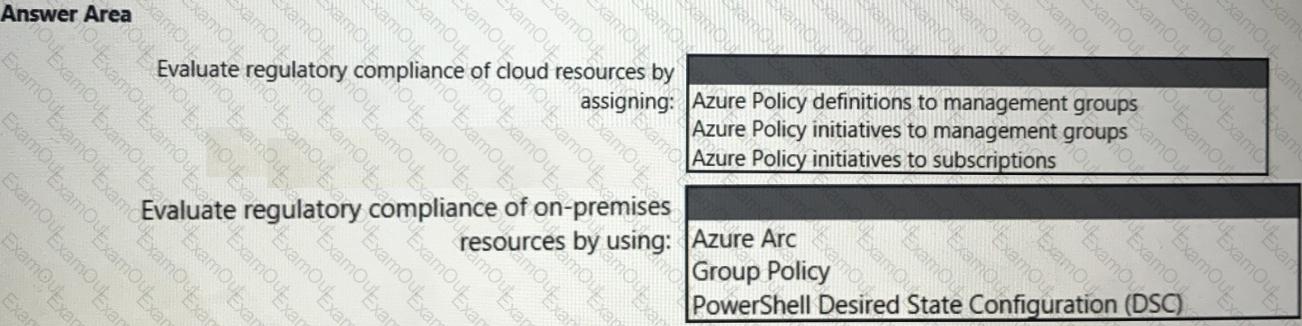
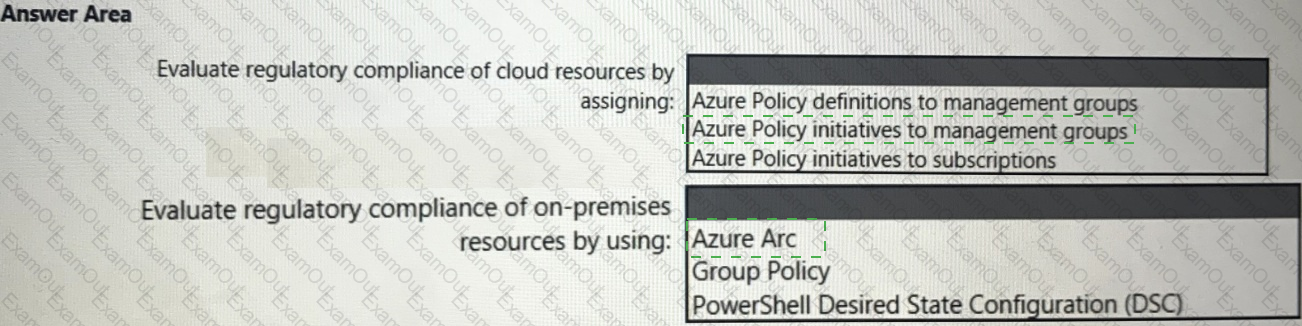
You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company has 10 branch offices. Each office has a local internet connection that uses a static IP address.
You have an Azure subscription. The subscription contains a storage account named storage1 that stores blobs.
Users in the branch offices access the blobs via the internet.
You need to recommend a solution to ensure that the data in storage1 is accessible only from the branch office static IP addresses.
The solution must minimize costs.
What should include in the recommendation?
