
Match the FortiSIEM device type to its description. Select each FortiSIEM device type in the left column, hold and drag it to the blank space next to its corresponding description in the column on the right.
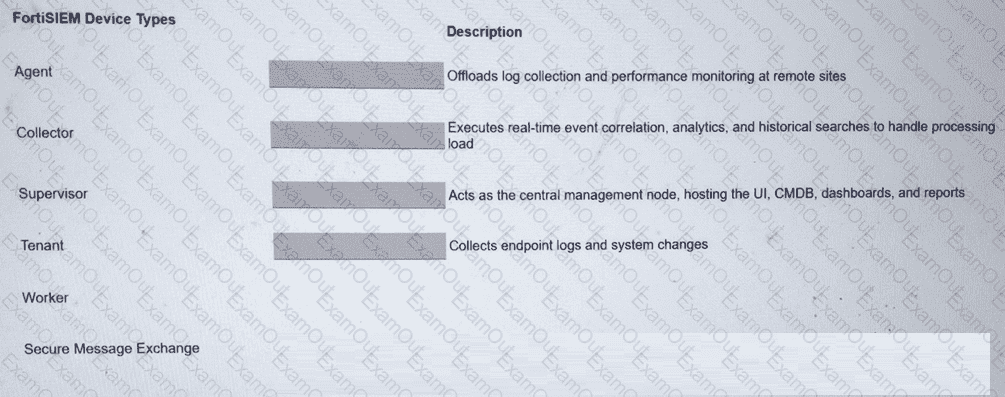
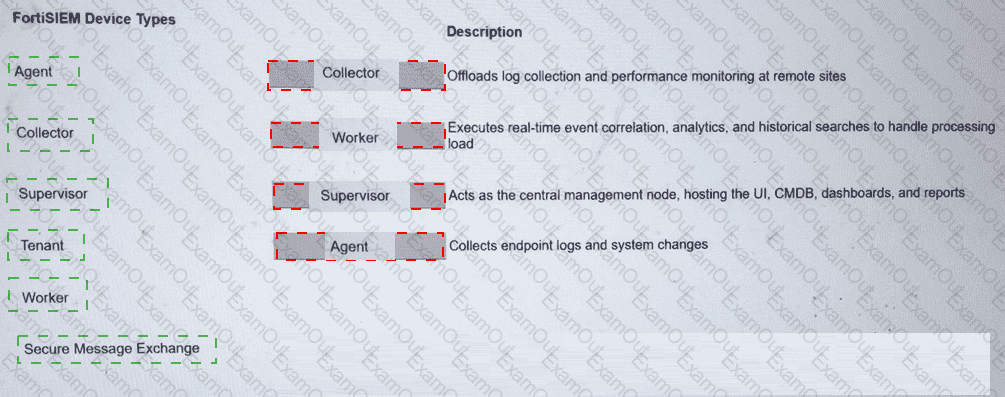
Refer to the exhibits.
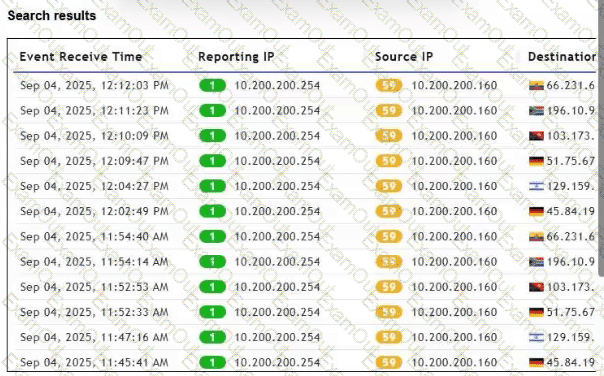
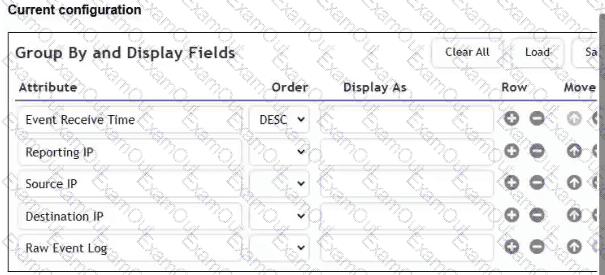
You are searching for permitted traffic to public destination IP addresses outside of North America. Your investigation shows that one local computer is communicating with destination IP addresses that fit the criteria. However, you also notice that some of those IP addresses are duplicates, and you must aggregate the results.
Which three steps do you need to use to configure the Group By and Display Fields window to show only aggregated results? (Choose three.)
Refer to the exhibit.
Which two options describe how the Update Asset and Identity Database playbook is configured? (Choose two.)
You configured a new module named Users. Next, you want to configure a playbook that creates users from ingested data. When new records are created, you want to ensure that duplicate users do not overwrite existing user records and their fields. However, you also want the playbook to continue running even if duplicates are encountered so that any non-duplicate records are still created. Which two actions fulfill the requirements? Choose two answers.
Which two types of variables can you use in playbook tasks? (Choose two.)
Which FortiAnalyzer connector can you use to run automation stitches9
Which two ways can you create an incident on FortiAnalyzer? (Choose two.)
You are trying to create a playbook that uses source data from ingestion to populate the description field of a task. You successfully saved the source data to a variable called ingestion_data. Now, you must parse the results and extract a list of indicators. Which Jinja expression can accomplish this task? Choose one answer.
