Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

Refer to the exhibit.
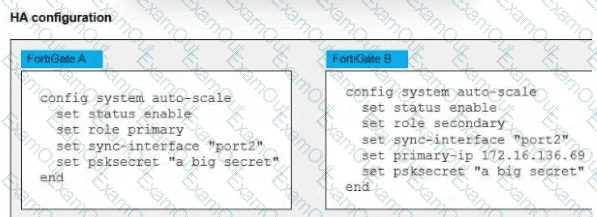
question 11

An administrator deployed an HA active-active load balance sandwich in Microsoft Azure. The setup requires configuration synchronization between devices.

What can you conclude from the configured settings shown in the exhibit? (Choose two.)

A.

By default, FortiGate uses FGCP.

B.

FortiGate-VM instances are scaled out automatically according to predefined workload levels.

C.

FortiGate A and FortiGate B are two independent devices.

D.

It does not synchronize the FortiGate hostname.

You must add an Amazon Web Services (AWS) network access list (NACL) rule to allow SSH traffic to a subnet for temporary testing purposes. When you review the current inbound and outbound NACL rules, you notice that the rules with number 5 deny SSH and telnet traffic to the subnet.

What can you do to allow SSH traffic?

A.

You do not have to create any NACL rules because the default security group rule automatically allows SSH traffic to the subnet.

B.

You must create a new allow SSH rule anywhere in the network ACL rule base to allow SSH traffic.

C.

You must create two new allow SSH rules, each with a number bigger than 5.

D.

You must create two new allow SSH rules, each with a number smaller than 5.

An administrator is configuring a software-defined network (SDN) connector in FortiWeb to dynamically obtain information about existing objects in an Amazon Elastic Kubernetes Service (EKS) cluster.

Which AWS policy should the administrator attach to a user to achieve this goal?

A.

AmazonEKSConnectorServiceRolePolicy

B.

AmazonEKSComputePolicy

C.

AmazonEKSServicePolicy

D.

AmazonEKSClusterPolicy

You are experiencing intermittent connectivity issues in a FortiGate HA cluster deployed with Azure gateway load balancer. Traffic is being dropped when it passes through the cluster. What is the cause of the issue? (Choose one answer)1

A.

The FortiGate firewalls are using the default maximum transmission unit (M2TU) size supported by Azure.

B.

The Azure gateway load balancer is configured with an incorrect health probe port.

C.

The Azure gateway load balancer is blocking large packets, causing traffic failures.

D.

The protected VMs are running an application that fragments packets.

What are two main features in Amazon Web Services (AWS) network access control lists (NACLs)? (Choose two answers)

A.

NACLs are stateless, and inbound and outbound rules are used for traffic filtering.

B.

NACLs are tied to an instance.

C.

The default NACL is configured to allow all traffic.

D.

You cannot use NACLs and Security Groups at the same time.

A customer would like to use FortiGate fabric integration with FortiCNP. When adding a FortiGate VM to FortiCNP, which three mandatory configuration steps must you follow on FortiGate? (Choose three answers)

A.

Enable pre-shared key on both sides.

B.

Import the FortiGate certificate into FortiCNP.

C.

Configure FortiGate to send logs to FortiCNP.

D.

Create an IPS sensor and a firewall policy.

E.

Create an SSL/SSH inspection profile.

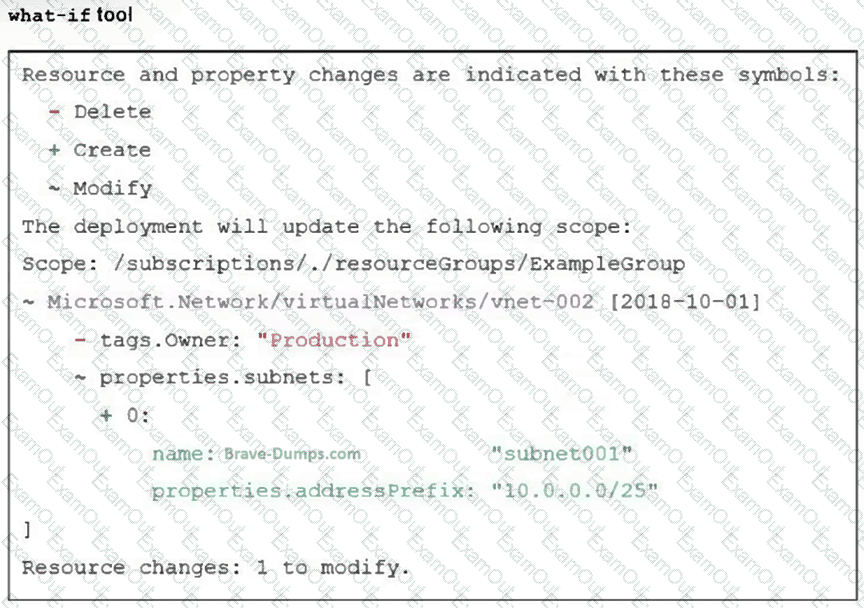
Refer to the exhibit.

question 17

An administrator used the what-if tool to preview the changes to an Azure Bicep file. What will happen if the administrator applies these changes in Azure? (Choose one answer)

A.

A new subnet will be added to vnet-002.

B.

The vnet-002 VNet will be renamed Production.

C.

The resulting VNet will have a single subnet.

D.

The VNet address space will be updated.

How does an administrator secure container environments in Amazon AWS from newly emerged security threats? (Choose one answer)

A.

Using Docker-related application control signatures.

B.

Using Amazon AWS-related application control signatures.

C.

Using distributed network-related application control signatures.

D.

Using Amazon AWS_S3-related application control signatures.

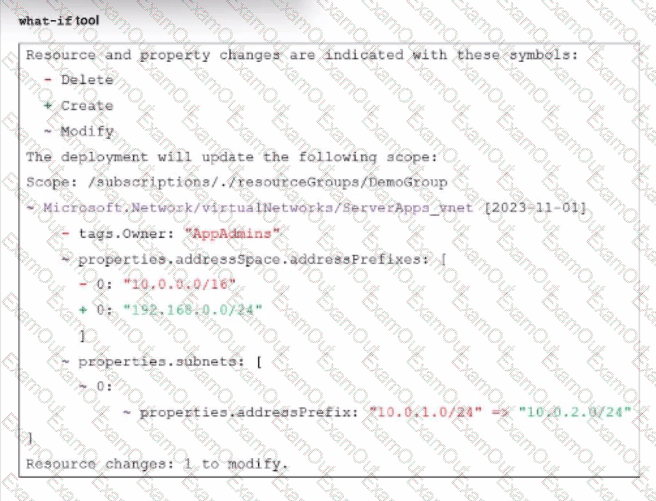
Refer to the exhibit.

question 19

An administrator used the what-if tool to preview changes to an Azure Bicep file.

What will happen if the administrator decides to apply these changes in Azure?

A.

Subnet 10.0.1.0/24 will replace subnet 10.0.2.0/24.

B.

This deployment will fail and no changes will be applied.

C.

A new subnet will be added to ServerApps.

D.

The ServerApps VNet will be renamed.

The cloud administration team is reviewing an AWS deployment that was done using CloudFormation.

The deployment includes six FortiGate instances that required custom configuration changes after being deployed. The team notices that unwanted traffic is reaching some of the FortiGate instances because the template is missing a security group.

To resolve this issue, the team decides to update the JSON template with the missing security group and then apply the updated template directly, without using a change set.

What is the result of following this approach?

A.

If new FortiGate instances are deployed later they will include the updated changes.

B.

Some of the FortiGate instances may be deleted and replaced with new copies.

C.

The update is applied, and the security group is added to all instances without interruption.

D.

CloudFormation rejects the update and warns that a new full stack is required.