Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

An engineer is investigating connectivity problems on Cisco Firepower that is using service group tags. Specific devices are not being tagged correctly, which is preventing clients from using the proper policies when going through the firewall How is this issue resolved?

A.

Use traceroute with advanced options.

B.

Use Wireshark with an IP subnet filter.

C.

Use a packet capture with match criteria.

D.

Use a packet sniffer with correct filtering

An engineer is deploying failover capabilities for a pair of Cisco Secure Firewall devices. The core switch keeps the MAC address of the previously active unit in the ARP table. Which action must the engineer take to minimize downtime and ensure that network users keep access to the internet after a Cisco Secure Firewall failover?

A.

Set the same MAC address on both units.

B.

Add the MAC address to the switch ARP table.

C.

Run a script to send gratuitous ARP after a failover.

D.

Use a virtual MAC address on both units.

What is the RTC workflow when the infected endpoint is identified?

A.

Cisco ISE instructs Cisco AMP to contain the infected endpoint.

B.

Cisco ISE instructs Cisco FMC to contain the infected endpoint.

C.

Cisco AMP instructs Cisco FMC to contain the infected endpoint.

D.

Cisco FMC instructs Cisco ISE to contain the infected endpoint.

Which two considerations must be made when deleting and re-adding devices while managing them via Cisco FMC (Choose two).

A.

Before re-adding the device In Cisco FMC, the manager must be added back.

B.

The Cisco FMC web interface prompts users to re-apply access control policies.

C.

Once a device has been deleted, It must be reconfigured before it is re-added to the Cisco FMC.

D.

An option to re-apply NAT and VPN policies during registration is available, so users do not need to re-apply the polices after registration is completed.

E.

There is no option to re-apply NAT and VPN policies during registration is available, so users need to re-apply the policies after registration is completed.

A security engineer must deploy a Cisco FTD appliance as a bump in the wire to detect intrusion events without disrupting the flow of network traffic. Which two features must be configured to accomplish the task? (Choose two.)

A.

inline set pair

B.

transparent mode

C.

tapemode

D.

passive interfaces

E.

bridged mode

A user within an organization opened a malicious file on a workstation which in turn caused a ransomware attack on the network. What should be configured within the Cisco FMC to ensure the file is tested for viruses on a sandbox system?

A.

Capacity handling

B.

Local malware analysis

C.

Spere analysis

D.

Dynamic analysis

Which feature issupportedby IRB on Cisco FTD devices?

A.

redundant interface

B.

dynamic routing protocol

C.

EtherChannel interface

D.

high-availability cluster

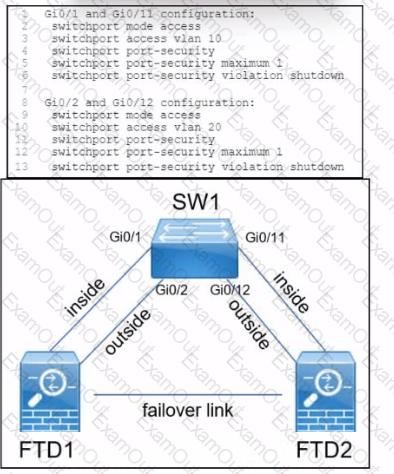
Refer to the exhibit.

question 68

A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?

A.

Disable port security on the switch interfaces connected to FTD1 and FTD2.

B.

Set maximum secured addresses to two on the switch interfaces on FTD1 and FTD2.

C.

Connect and configure a stateful link and thon deploy the changes.

D.

Configure the spanning-tree PortFasI feature on SW1 and FTD2

An engineer installs a Cisco FTD device and wants to inspect traffic within the same subnet passing through a firewall and inspect traffic destined to the internet.

Which configuration will meet this requirement?

A.

transparent firewall mode with IRB only

B.

routed firewall mode with BVI and routed interfaces

C.

transparent firewall mode with multiple BVIs

D.

routed firewall mode with routed interfaces only

An administrator receives reports that users cannot access a cloud-hosted web server. The access control policy was recently updated with several new policy additions and URL filtering. What must be done to troubleshoot the issue and restore access without sacrificing the organization ' s security posture?

A.

Create a new access control policy rule to allow ports 80 and 443 to the FQDN of the web server.

B.

Identify the blocked traffic in the Cisco FMC connection events to validate the block, and modify the policy to allow the traffic to the web server.

C.

Verify the blocks using the packet capture tool and create a rule with the action monitor for the traffic.

D.

Download a PCAP of the traffic attempts to verify the blocks and use the flexconfig objects to create a rule that allows only the required traffic to the destination server.