Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?

A.

Restore the primary Cisco FMC backup configuration to the secondary Cisco FMC device when the primary device fails.

B.

Configure high-availability in both the primary and secondary Cisco FMCs.

C.

Connect the primary and secondary Cisco FMC devices with Category 6 cables of not more than 10 meters in length.

D.

Place the active Cisco FMC device on the same trusted management network as the standby device.

A network administrator configured a NAT policy that translates a public IP address to an internal web server IP address. An access policy has also been created that allows any source to reach the public IP address on port 80. The web server is still not reachable from the Internet on port 80. Which configuration change is needed?

A.

The intrusion policy must be disabled for port 80.

B.

The access policy rule must be configured for the action trust.

C.

The NAT policy must be modified to translate the source IP address as well as destination IP address.

D.

The access policy must allow traffic to the internal web server IP address.

A Cisco FMC administrator wants to configure fastpathing of trusted network traffic to increase performance. In which type of policy would the administrator configure this feature?

A.

Identity policy

B.

Prefilter policy

C.

Network Analysis policy

D.

Intrusion policy

Refer to the exhibit.

A systems administrator conducts a connectivity test to their SCCM server from a host machine and gets no response from the server. Which action ensures that the ping packets reach the destination and that the host receives replies?

A.

Create an access control policy rule that allows ICMP traffic.

B.

Configure a custom Snort signature to allow ICMP traffic after Inspection.

C.

Modify the Snort rules to allow ICMP traffic.

D.

Create an ICMP allow list and add the ICMP destination to remove it from the implicit deny list.

An engineer is troubleshooting the upgrade of a Cisco Secure Firewall Threat Defense device on the Secure Firewall Management Center 7.0 GUI. The engineer wants to collect the upgrade data and logs. Which two actions must the engineer take? (Choose two.)

A.

View the system and troubleshooting details.

B.

Select the Secure Firewall Threat Defense device properties.

C.

Select the Secure Firewall Management Center device.

D.

Access the Health Events page.

E.

Access the Health Monitor page.

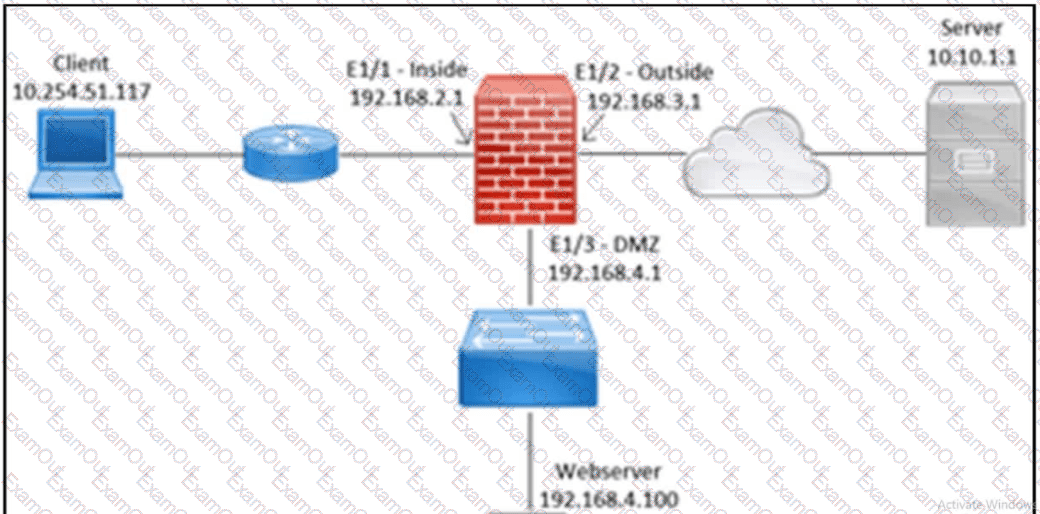
Refer to the exhibit.

question 56

A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?

A.

Configure the inside interface to send ACK messages.

B.

Add a firewall rule that allows the web server to communicate with the DMZ.

C.

Add a firewall rule that allows ACK responses from the inside to the outside.

D.

Configure the outside interface to receive SYN-ACK messages.

A network engineer sets up a secondary CiscoFMC that is integrated with Cisco Security Packet Analyzer What occurs when the secondary CiscoFMC synchronizes with the primary Cisco FMC?

A.

The existing integration configuration is replicated to the primary Cisco FMC

B.

The existing configuration for integration of the secondary Cisco FMC the Cisco Security Packet Analyzer is overwritten.

C.

The synchronization between the primary and secondary Cisco FMC fails

D.

The secondary Cisco FMC must be reintegrated with the Cisco Security Packet Analyzer after the synchronization

Which Cisco Firepower feature is used to reduce the number of events received in a period of time?

A.

rate-limiting

B.

suspending

C.

correlation

D.

thresholding

Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)

A.

BGPv6

B.

ECMP with up to three equal cost paths across multiple interfaces

C.

ECMP with up to three equal cost paths across a single interface

D.

BGPv4 in transparent firewall mode

E.

BGPv4 with nonstop forwarding

A network administrator notices that remote access VPN users are not reachable from inside the network. It is determined that routing is configured correctly, however return traffic is entering the firewall but not leaving it What is the reason for this issue?

A.

A manual NAT exemption rule does not exist at the top of the NAT table.

B.

An external NAT IP address is not configured.

C.

An external NAT IP address is configured to match the wrong interface.

D.

An object NAT exemption rule does not exist at the top of the NAT table.