
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

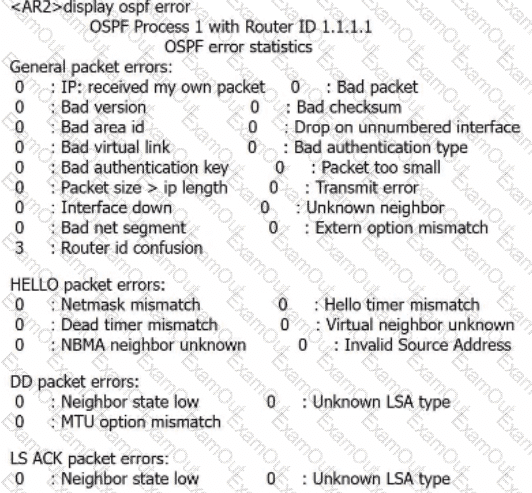
On an OSPF network, two directly connected routers fail to establish a neighbor relationship. The display ospf error command is run on one of the routers, and the command output is as follows:
question 101

Based on the command output, which of the following is the cause of the problem?

A.

OSPF Auth Types are the same.

B.

OSPF router IDs are the same.

C.

OSPF area IDs are the same.

D.

OSPF Auth Data values are the same.

An enterprise uses OSPF to implement network communication. To ensure data validity and security, all authentication modes supported by OSPF are enabled on routers. In this case, interface authentication is preferentially used by the routers.

A.

TRUE

B.

FALSE

After IPsec is deployed on an enterprise network, services are interrupted. The administrator finds that no data flow triggers IKE negotiation.

Which of the following are possible causes? (Select all that apply)

A.

Configuration error of an interzone security policy

B.

An unreachable route

C.

The IPsec policy is not correctly applied to the related interface.

D.

A mismatch between the ACL and protected data flow

Which of the following statements regarding the stateful inspection firewall is true?

A.

When the stateful inspection firewall checks packets, packets of one same connection are not correlated.

B.

Because UDP is a connectionless protocol, so the stateful inspection firewall cannot match UDP packets with the status table.

C.

The stateful inspection firewall only needs to match the first data packet against a rule, and the subsequent packets of the connection are matched directly in the state table.

D.

The stateful inspection firewall needs to match the rules for each incoming packet.

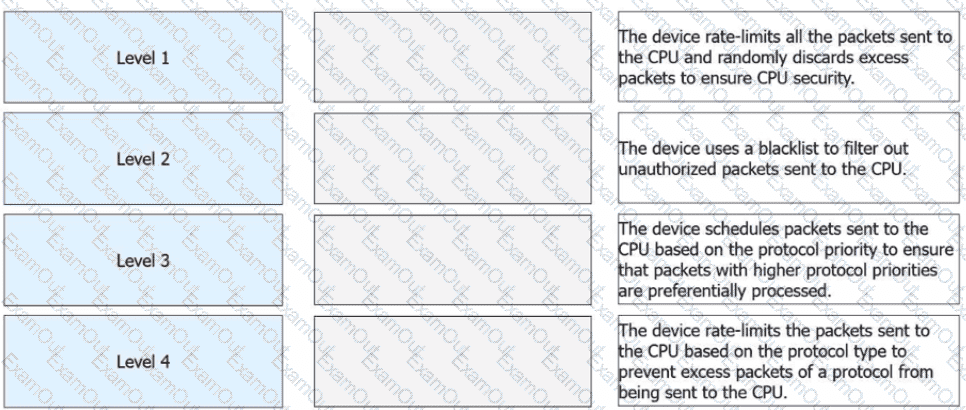
CPU attack defense uses a multi-level security mechanism to implement hierarchical device protection. Match the following levels with the corresponding protection functions.
question 105

Security policy is the core feature of firewalls. Only valid traffic that complies with security policies can be forwarded by firewalls. Which of the following statements are true about security policy matching rules?

A.

Multiple values can be configured for a single matching condition, and the values are logically ANDed.

B.

If a security policy contains multiple matching conditions, the relationship between them is AND.

C.

The system has a default security policy named default, where all matching conditions are any and the default action is permit.

D.

When multiple security policy rules are configured, they are sorted in a list by configuration sequence by default. A security policy rule configured earlier is placed higher in the list and has a higher priority.

Route summarization can effectively reduce the number of BGP routes. However, many parameters need to be properly set when configuring BGP route summarization. Otherwise, problems such as routing loops may occur.

Which of the following statements is false about BGP route summarization?

A.

If the aggregate command with suppress-policy specified is run on a device, the device advertises only the specific routes that match the given routing policy.

B.

If the aggregate command is run on a device, the device advertises both specific and summary routes.

C.

If the summary automatic command is run on a device, the device summarizes subnet routes based on natural network segments.

D.

If the aggregate command with detail-suppressed specified is run on a device, the device advertises only the summary route.

IGMPv2 uses the timeout mechanism for group members leaving a group. Group members can only leave a group silently. Before the timeout period expires, multicast traffic is still forwarded by the multicast router, and this is a defect.

A.

TRUE

B.

FALSE