Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)

A.

A FortiLink interface must be enabled on FortiGate.

B.

The switch controller feature must be enabled on FortiGate.

C.

Only a hardware-based FortiGate can manage a FortiSwitch stack.

D.

FortiSwitch must be operating in standalone mode before authorization.

Refer to the exhibit.

question 22

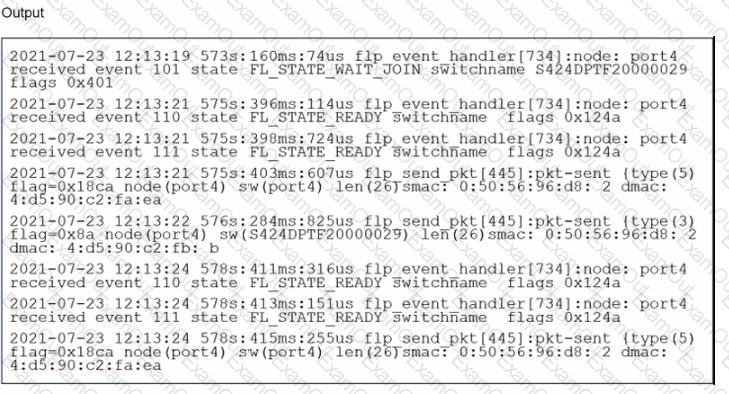
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)

A.

FortiSwitch is sending FortiLink heartbeats to FortiGate.

B.

FortiSwitch is discovered and authorized by FortiGate.

C.

FortiSwitch is in a waiting state to join the stack group on FortiGate.

D.

FortiSwitch is ready to push its new hostname to FortiGate.

Refer to the exhibits.

question 23

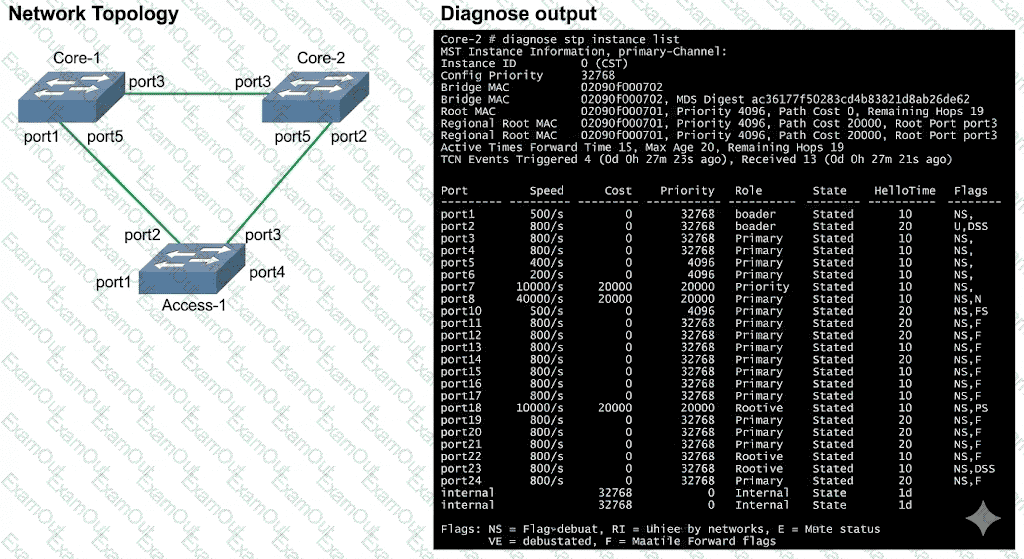
Three FortiSwitch devices in standalone mode are interconnected. The CLI command diagnose stp instance list is executed on Core-2. Based on the output shown in the exhibit, what can you conclude about Core-2? (Choose one answer)

A.

Core-2 has received Bridge Protocol Data Unit (BPDU) from the root bridge.

B.

Core-2 is the designated bridge for all VLANs.

C.

Core-2 is blocking all ports in the Spanning Tree Protocol (STP) topology.

D.

Core-2 provides an alternate path to the root bridge.

What does the switchauto-networksetting control on FortiSwitch? (Choose one answer)

A.

The automatic VLAN assignment based on connected devices

B.

The automatic discovery of the FortiGate- > FortiLink interface

C.

The root bridge priority for Multiple Spanning Tree Protocol (MSTP)

D.

Whether the FortiSwitch can be managed by FortiManager

How are the ' by VLAN redirect MAC address quarantine ' mode and the ' by redirect MAC address quarantine ' mode on FortiGate similar?

A.

Both modes move quarantined devices to the quarantine VLAN.

B.

Both modes require firewall policies to block inter-VLAN traffic.

C.

Both modes add quarantined device MAC addresses to the blocked firewall address group.

D.

Both modes block intra-VLAN traffic by FortiGate automatically.

Refer to the exhibit.

question 26

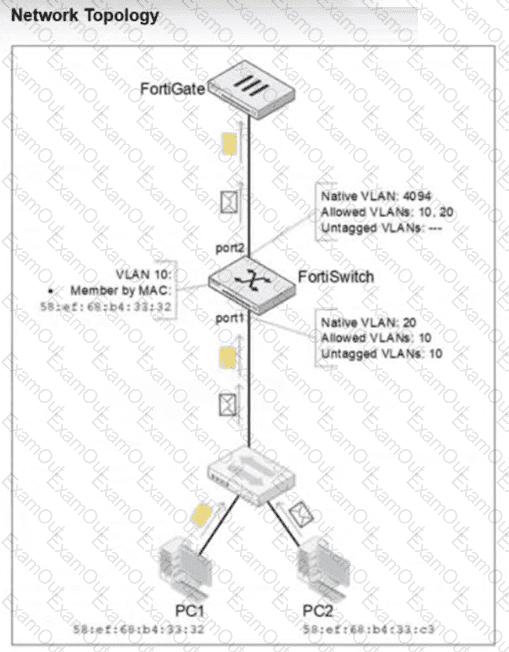
PC1 and PC2 are connected to port1 on FortiSwitch. Which VLAN tags will FortiSwitch apply when forwarding PC1 and PC2 traffic out of port2? (Choose one answer)

A.

FortiSwitch will tag PC1 and PC2 frames with VLAN 20.

B.

FortiSwitch will tag both PC1 and PC2 frames with VLAN 10, due to MAC override.

C.

FortiSwitch will tag PC1 frames with VLAN 10 and PC2 frames with VLAN 20.

D.

FortiSwitch will leave PC1 frames untagged and will tag PC2 frames with VLAN 10.

Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three answers)

A.

Assign the VLAN ID

B.

Quarantine devices

C.

Traffic processing

D.

Set outer VLAN tags

E.

QoS

How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?

A.

Only high-end FortiSwitch models support ACL.

B.

ACL can be used only at the prelookup stage in the traffic processing pipeline.

C.

Classifiers enable matching traffic based only on the VLAN ID.

D.

FortiSwitch checks ACL policies only from top to bottom.

Refer to the exhibits.

question 29

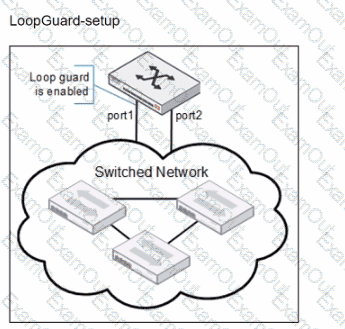
Port1 and port2 are the only ports configured with the same native VLAN 10.

What are two reasons that can trigger port1 to shut down? (Choose two.)

A.

port1 was shut down by loop guard protection.

B.

STP triggered a loop and applied loop guard protection on port1.

C.

An endpoint sent a BPDU on port1 that it received from another interface.

D.

Loop guard frame sourced from port 1 was received on port 1.

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices