A loan company compares a machine learning model that was found on the dark web with the company ' s proprietary model. Using proprietary information, the company generates the following:
Input
Dark web model
Company ' s proprietary model
Jane A.
Approve
Approve
John B.
Deny
Deny
Ann J.
Deny
Deny
Joe H.
Approve
Approve
Which of the following should the AI red team recommend to mitigate risks for future deployments?
An architect is using the firm ' s recommended large language model (LLM) to find an internal solution for content management.
Given the following:
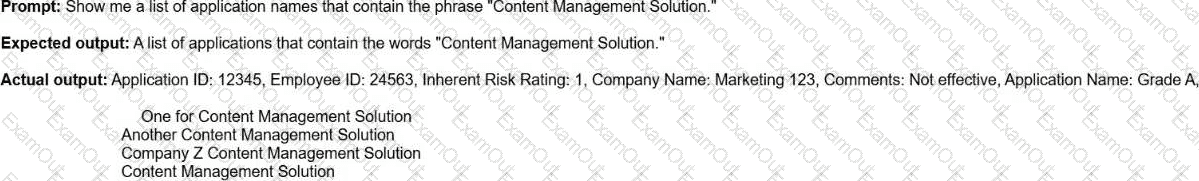
Which of the following controls is the best for mitigating this issue?
A team of engineers builds an application using a large language model (LLM). The application is built on Linux and is hosted on a virtual server. Users must create an account in order to access and use the platform.
Which of the following should the team do to protect the account credentials?
During a model validation procedure, an engineer notices that a model performs well during training but poorly during testing.
Which of the following best describes the reason?
A company introduces a large language model (LLM) in an application in order to monitor for a potential denial-of-service attack. Which of the following should the company use to measure the utilization of the LLM?
An analyst wants to develop a solution to review security information and event management (SIEM) logs for endpoint analytics. Which of the following is a benefit of a small language model (SLM) compared to a large language model (LLM) when cost efficiency is a consideration?
A security analyst notices that regardless of user-submitted prompts, an AI model always returns unsanitized responses. These responses are then passed to multiple plug-ins. The analyst is concerned with the potential security implications.
Which of the following Open Worldwide Application Security Project (OWASP) categories addresses this vulnerability?