An engineer is configuring a new Cisco ISE node. The Device Admin service must run on this node to handle authentication requests for network-device access through TACACS+. Which persona must be enabled on this node to perform this function?
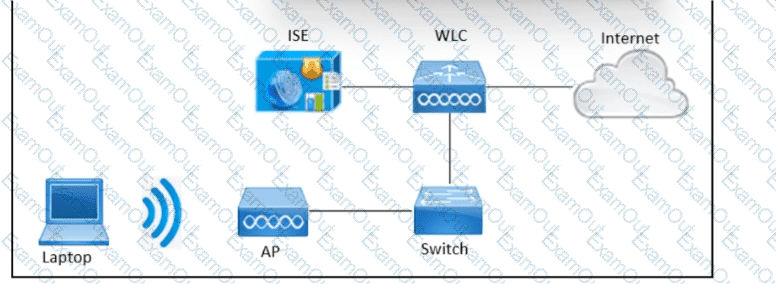
Refer to the exhibit. An engineer needs to configure central web authentication on the Cisco Wireless LAN Controller to use Cisco ISE for all guests connected to the wireless network. The components are configured already:
• Cisco Wireless LAN Controller is fully configured
• authorization profile on the Cisco ISE
• authentication policy on the Cisco ISE
Which component would be configured next on Cisco ISE?
A network security engineer needs to configure 802.1X port authentication to allow a single host to be authenticated for data and another single host to be authenticated for voice. Which command should the engineer run on the interface to accomplish this goal?
An engineer is deploying Cisco ISE in a network that contains existing security products from Cisco and other vendors. The customer requires support for Cisco TrustSec and the sharing of security group tags and policy objects between Cisco ISE and the other production security products. Which persona type must be enabled on one of the Cisco ISE nodes?
Which default " guest type " is included with Cisco ISE?
A security administrator is using Cisco ISE to create a BYOD onboarding solution for all employees who use personal devices on the corporate network. The administrator generates a Certificate Signing Request and signs the request using an external Certificate Authority server. Which certificate usage option must be selected when importing the certificate into ISE?
A network engineer is configuring a Cisco Wireless LAN Controller in order to find out more information about the devices that are connecting. This information must be sent to Cisco ISE to be used in authorization policies. Which profiling mechanism must be configured in the Cisco Wireless LAN Controller to accomplish this task?
An administrator replaced a PSN in the distributed Cisco ISE environment. When endpoints authenticate to it, the devices are not getting the right profiles or attributes and as a result, are not hitting the correct policies. This was working correctly on the previous PSN. Which action must be taken to ensure the endpoints get identified?
Which personas can a Cisco ISE node assume ' ?
A laptop was stolen and a network engineer added it to the block list endpoint identity group What must be done on a new Cisco ISE deployment to redirect the laptop and restrict access?