For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?
A Splunk administrator needs to integrate a third-party vulnerability management tool to automate remediation workflows. What is the most efficient first step?
The Director of Security would like to understand the operational efficiency of the SOC analysts at a high level. What is a metric that can be used to determine their efficiency?
Based on the provided screenshot, different machines or accounts have been associated with chosen threat objects. Which two Enterprise Security frameworks are responsible for programmatically associating this information?
Which fields are used to determine asset priority, when priority is assigned through an asset and identity lookup?
What is one method used in ESCU content to calculate a risk score when creating a detection that uses the Risk Analysis adaptive response action?
What framework in Enterprise Security allows engineers to build detections using known malicious IOCs, comparing them to event logs to find suspicious behavior?
Which tool can help provide a baseline of the data sources in a given Splunk environment?
Based on the provided screenshot, it ' s discovered that different machines or accounts have been associated with the shown threat objects.
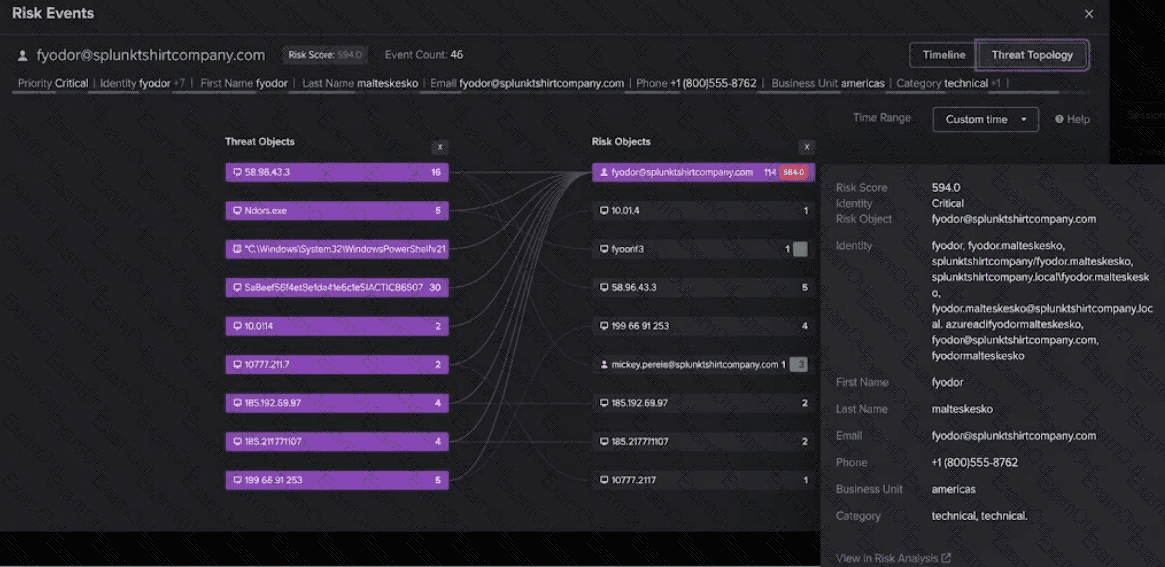
Enterprise Security has identified that these machines and accounts all point back to one owner - Fyodor. Which two frameworks in ES are responsible for programmatically associating this information together?
What is a key feature of effective security reports for stakeholders?