Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

Which three FortiSASE use cases are possible? (Choose three answers)

A.

Secure Internet Access (SIA)

B.

Secure SaaS Access (SSA)

C.

Secure Private Access (SPA)

D.

Secure VPN Access (SVA)

E.

Secure Browser Access (SBA)

Refer to the exhibit.

question 2

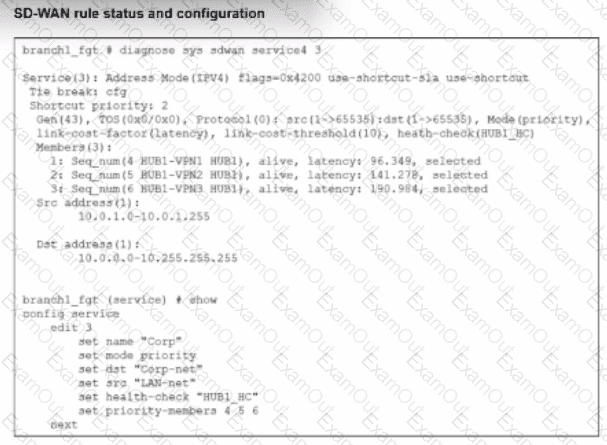
The SD-WAN rule status and configuration is shown. Based on the exhibit, which change in the measured latency will first make HUB1-VPN3 the new preferred member?

A.

When HUB1-VPN3 has a latency of 80 ms

B.

When HUB1-VPN3 has a lower latency than HUB1-VPN1 and HUB1-VPN2

C.

When HUB1-VPN1 has a latency of 200 ms

D.

When HUB1-VPN3 has a latency of 90 ms

Which two delivery methods are used for installing FortiClient on a user ' s laptop? (Choose two.)

A.

Use zero-touch installation through a third-party application store.

B.

Download the installer directly from the FortiSASE portal.

C.

Send an invitation email to selected users containing links to FortiClient installers.

D.

Configure automatic installation through an API to the user ' s laptop.

Refer to the exhibit.

question 4

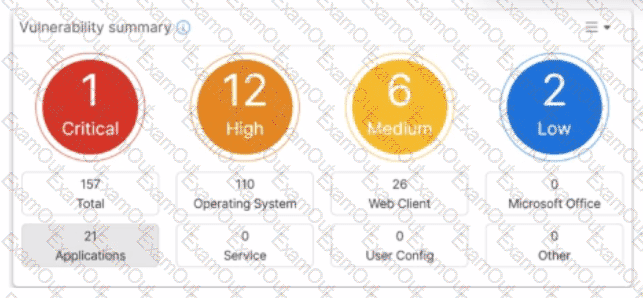
Which two statements about the Vulnerability summary dashboard in FortiSASE are correct? (Choose two.)

A.

The dashboard shows the vulnerability score for unknown applications.

B.

Vulnerability scan is disabled in the endpoint profile.

C.

The dashboard allows the administrator to drill down and view CVE data and severity classifications.

D.

Automatic vulnerability patching can be enabled for supported applications.

What is a key use case for FortiSASE Secure Internet Access (SIA) in an agentless deployment? (Choose one answer)

A.

It provides secure web browsing by isolating browser sessions and enforcing data loss prevention for temporary employees.

B.

It acts as a secure web gateway (SWG) distributing a PAC file for explicit web proxy use, securing HTTP and HTTPS traffic with a full security stack, and is ideal for unmanaged endpoints like contractors.

C.

It distributes a PAC file to secure non-web traffic protocols and applies antivirus protection only for managed endpoints.

D.

It requires FortiClient endpoints and supports ZTNA tags to secure all network traffic for unmanaged endpoints.

Which two configurations are required for Agentless ZTNA to work? (Choose two.)

A.

Proxy user single sign-on (SSO)

B.

FortiGate with ZTNA proxy

C.

FortiClient Agent

D.

SD-WAN Private Access (SPA)

Which three reports are valid report types in FortiSASE? (Choose three.)

A.

Web Usage Summary Report

B.

Endpoint Compliance Deviation Report

C.

Vulnerability Assessment Report

D.

Shadow IT Report

E.

Cyber Threat Assessment

You are configuring SD-WAN to load balance network traffic. Which two facts should you consider when setting up SD-WAN? (Choose two.)
A.

When applicable, FortiGate load balances traffic through all members that meet the SLA target.

B.

SD-WAN load balancing is possible only when using the manual and the best quality strategies.

C.

Only the manual and lowest cost (SLA) strategies allow SD-WAN load balancing.

D.

You can select the outsessions hash mode with all strategies that allow load balancing.

question 9

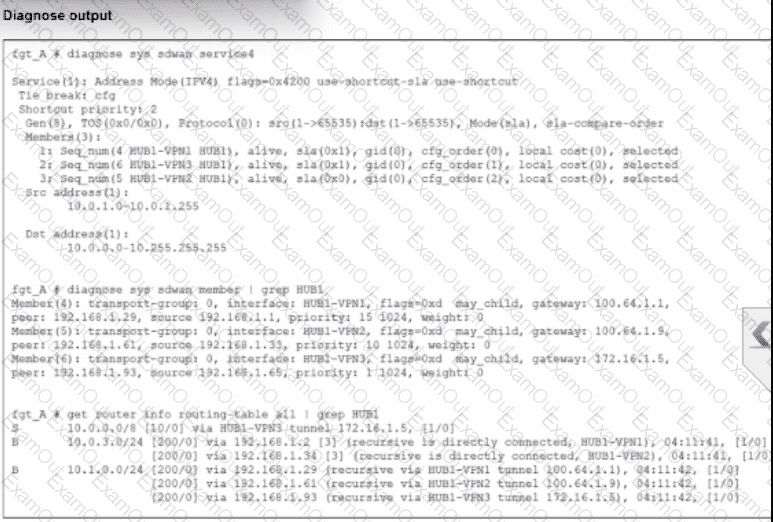
An administrator is troubleshooting SD-WAN on FortiGate. A device behind branch1_fgt generates traffic to the 10.0.0.0/8 network. The administrator expects the traffic to match SD-WAN rule ID 1 and be routed over HUB1-VPN1. However, the traffic is routed over HUB1-VPN3.

Based on the output shown in the exhibit, which two reasons, individually or together, could explain the observed behavior? (Choose two.)

A.

HUB1-VPN1 does not have a valid route to the destination.

B.

HUB1-VPN3 has a higher member configuration priority than HUB1-VPN1.

C.

HUB1-VPN3 has a lower route priority value (higher priority) than HUB1-VPN1.

D.

The traffic matches a regular policy route configured with HUB1-VPN3 as the outgoing device.

Refer to the exhibit.

question 10

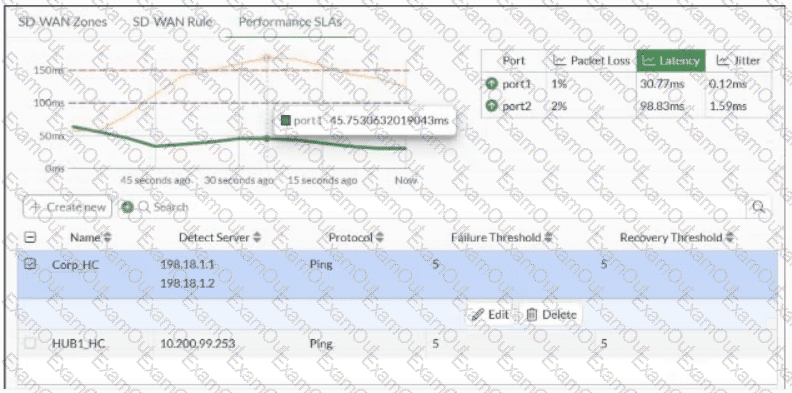
Which conclusion can you draw from the exhibit?

A.

Over the past 60 seconds, the member port2 latency was temporarily above the latency criteria defined for HUB1_HC.

B.

The administrator configured the Corp_HC performance service-level agreement (SLA) with SLA targets for the three criteria: packet loss, latency, and jitter.

C.

Over the past 60 seconds, the member port1 was monitored healthy for both latency criteria of the Corp_HC definition.

D.

The administrator configured the packet loss threshold for Corp_HC and HUB1_HC to 5%.