Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: estly75

Which of the following is the most important reason why tactics, techniques, and procedures (TTP) are beneficial to a defensive strategy?

A.

TTP provides useful insights on the hash values and internet protocol addresses attributed to an attacker.

B.

TTP provides useful insights on an attacker's indicators of compromise.

C.

TTP provides useful insights on the tools used by an attacker.

D.

TTP provides useful insights on the strategy and behavior of an attacker.

An analyst reviews the following log entries:
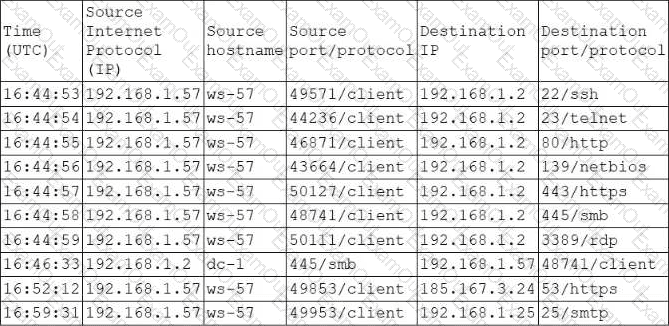
Which of the following conclusions should the analyst reach? (Choose two.)

A.

Host ws-57 is performing a network scan against dc-1.

B.

Domain Controller dc-1 is performing a network scan against ws-57.

C.

Host ws-57 delivered a phishing email via Simple Mail Transfer Protocol.

D.

Host ws-57 is communicating on a service using a non-standard port.

E.

Domain Controller dc-1 is infected with ransomware and initiating connections with ws-57.

F.

Domain Controller dc-1 is communicating using a non-standard port.

A security analyst runs an Nmap scan against a host with multiple open ports using the following command:

nmap 10.10.10.1 -p-

The following output is obtained after the scan:

Starting Nmap 7.95 ( https://nmap.org ) at 2025-07-15 15:55 UTC

Note: Host seems down.

Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds

Which of the following is the most accurate way to scan the target IP for open ports?

A.

nmap 10.10.10.1 -p80, 443, 445, 9999, 135, 22, 21 -b --traceroute

B.

nmap -sn -p- 10.10.10.1

C.

nmap -p- -Pn 10.10.10.1

D.

nmap 10.10.10.1/24 -p- -R -O --script=ssl-enum-ciphers

A Chief Information Security Officer (CISO) evaluates a threat heat map and notices a substantial increase in custom scanning and enumeration activities. The CISO wants to gather as much information as possible about the activities targeting the company to help prioritize mitigations.

Which of the following solutions is the best way to accomplish this goal?

A.

Configuring a honeypot in a separate environment to gather attacker techniques

B.

Leveraging canary tokens on all production systems to detect valid intrusion attempts

C.

Subscribing to information-sharing and threat intelligence reports for the industry

D.

Implementing a web application firewall in front of all applications and having it log attacks

An analyst is configuring a security information and event management system to capture fileless malware execution events.

Which of the following log files requires additional configuration to accomplish this task?

A.

Microsoft-Windows-Crypto-DPAPI/Operational

B.

Microsoft-Windows-PowerShell/Operational

C.

Microsoft-Windows-UserPnp/DeviceInstall

D.

Microsoft-Windows-TerminalServices-LocalSessionManager/Operational

A security team deploys a new scanning solution that requires root, domain administrator, and local server administrator permissions on all systems.

Which of the following is the best way to help mitigate the risk for this level of access?

A.

Enabling single sign-on for all administrators

B.

Integrating token-based authentication using a privileged access management (PAM) solution

C.

Using temporary, one-time passwords as part of the login process

D.

Configuring agentless scanning for critical targets

A security analyst reruns infrastructure as code (IaC) to tear down and rebuild a new environment after a ransomware attack.

Which of the following describes this phase?

A.

Analysis

B.

Post-incident

C.

Detection

D.

Containment

E.

Recovery

An analyst receives an alert that a user clicked on a malicious link. The analyst verifies that the link is malicious and was intended to capture credentials. The analyst verifies that the user visited the website, but no evidence indicates that the credentials were used. The analyst recommends that the user take remedial training and closes the case.

Which of the following steps in the incident response process did the analyst neglect?

A.

Analysis

B.

Containment

C.

Recovery

D.

Post-incident

Which of the following occurs during the analysis phase of the incident response process?

A.

Triage

B.

Alert writing

C.

Reimaging

D.

Isolation

Which of the following is the most likely reason an organization might implement compensating controls?
A.

A vulnerability does not have a patch, and the system is mission critical.

B.

A vulnerability has been fixed, tested, and deployed to production.

C.

A vulnerability is being actively exploited in the wild, but the organization does not use the affected system.

D.

A vulnerability was detected, but the organization has determined the result is a false positive.